☧ N I X D A E M O N
A declarative NixOS offensive-security workstation, as one flake.
The successor to IceBreaker.





NixDaemon is a complete pentesting workstation declared in code: every tool, every helper script, the desktop, the shell and the theme come from this flake. One command builds the whole machine, and the same command rebuilds it identically anywhere else. A bad change is undone by booting the previous generation.
It is built for authorised work — HackTheBox, the CPTS path, labs and scoped engagements — and organised around that workflow: connect the VPN, open a box, scan, enumerate, catch a shell, record it all for the write-up.
$ htbup                                   # VPN up, shows your tunnel IP
$ htbbox new Sauna 10.10.10.175 win easy  # box directory + box.json + $TARGET + /etc/hosts
$ htbscan full                            # -p- then -sC -sV on what is open → recon/, box.json
$ revshell ps64 9001                      # base64 PowerShell for your tunnel IP
$ htbbox flag user 3f2a…                  # status follows: active → user → root

| Layer | What you get |
|---|---|
| Toolkit | 23 categories, each one switch. 12 on by default (the CPTS set): recon, AD, web, pivot, crack, shells, payloads, wordlists, BloodHound CE, Python/impacket, GUI tools, core. 11 more one line away: DFIR, reversing, wireless, radio, hardware, C2, database, cloud, OSINT, social, mobile. |
| HTB workflow | htbvpn/htbup (OpenVPN as a systemd unit), htbtarget ($TARGET in every terminal + /etc/hosts for Kerberos), htbtime (clock skew), htbbox (per-box tree and box.json), htbscan, revshell, hcmode, htbcast (session recording → write-up transcript), payload-serve |
| Arsenal | ~/pentesting/ with permanent $privesc $potatoes $mimikatz $ad $sharp $ligolo $chisel … variables and htbpaths to find things. ligolo-ng, chisel, fscan and pspy cross-compiled from source for every OS/arch; the potato family, SharpCollection, PEASS, mimikatz, static nmap/socat — every download pinned by hash. |
| Desktop | Niri (scrolling Wayland) + Noctalia shell in Rosé Pine by default. For VMs without 3D, two X11 desktops in Rosé Pine, off until you choose one: XFCE (full desktop) or i3 (lightweight tiling). Or headless + SSH. |
| VM support | guest tools for VMware, VirtualBox, QEMU/KVM/UTM and Hyper-V from one setting; VMware/VirtualBox shared folders with sharedFolders = true. |
| Claude Code skill | ~/.claude/skills/nixdaemon is installed for you, so claude knows how the system is built and how to troubleshoot it (skills/nixdaemon). |
| Shell | zsh, starship prompt with $TARGET, fzf, zoxide, kitty with tmux-style keys, Neovim (nvf), yazi. |
| Cards | pentest-cheat, niri-cheat, nix-cheat — the whole workflow in the terminal, section by section. |
| Tests | nix flake check: every category's binaries are resolved and run, impacket alias collisions are caught, and NixOS VM tests boot the VPN, target and clock helpers. |


| Minimum | Comfortable | |
|---|---|---|
| CPU | x86_64 or aarch64 | 4+ cores |
| RAM | 4 GB | 8–16 GB |
| Disk | 60 GB | 100 GB |
| Firmware | UEFI or legacy BIOS | UEFI, Secure Boot off |
| Runs on | bare metal · VMware · VirtualBox · QEMU/KVM · Proxmox · UTM · Parallels · Hyper-V |
On aarch64 everything works except BloodHound CE (switched off for you) and
the mobile category. Only want the tools on an existing Linux or WSL? See
Path C.

The full walk-through — partitioning, every hypervisor, an existing NixOS,
first boot, troubleshooting — is docs/install.md.
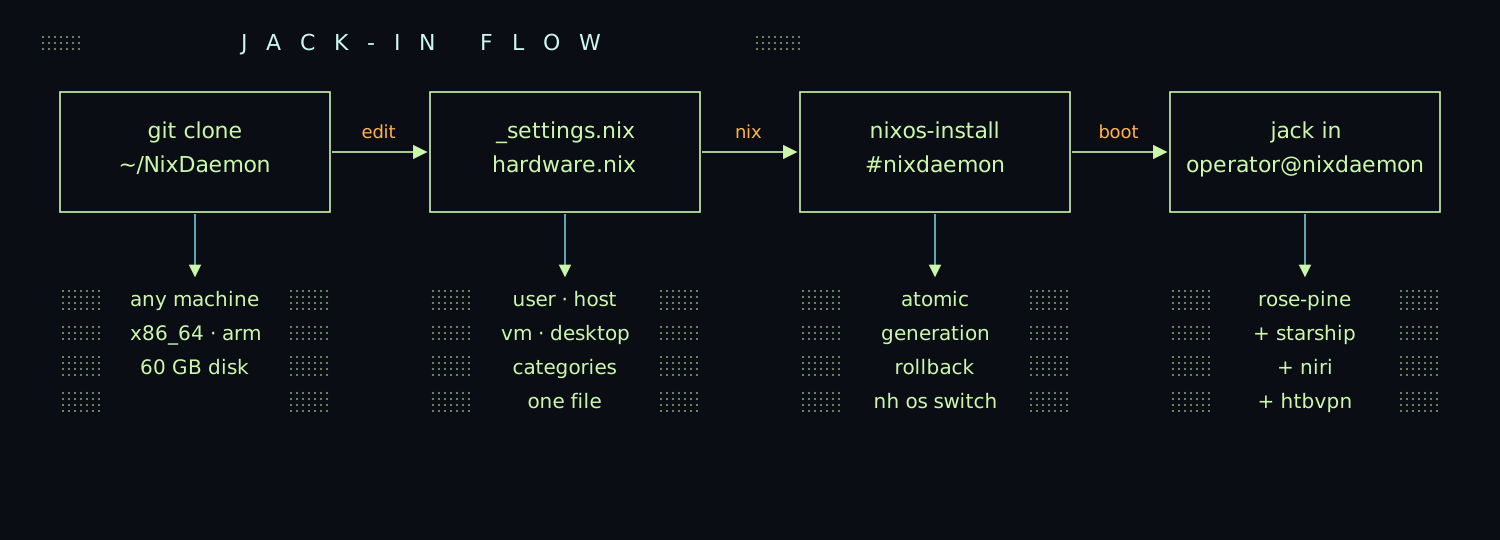
The short version, from the NixOS minimal ISO with your disk mounted at
/mnt:
nix-shell -p git
git clone https://gitlab.com/DAEMON-404/NixDaemon.git /mnt/home/operator/NixDaemon
cd /mnt/home/operator/NixDaemon

nano modules/hosts/generic/_settings.nix          # user, arch, boot mode, VM, desktop, categories
nixos-generate-config --root /mnt --show-hardware-configuration \
  > modules/hosts/generic/_hardware-configuration.nix

nixos-install --flake .#nixdaemon && reboot
Everything about your machine is in those two files. _settings.nix looks
like this:
{
  user = "operator";
  hostName = "nixdaemon";
  system = "x86_64-linux";   # or "aarch64-linux"
  boot = "efi";              # or "bios"
  vm = "none";               # vmware | virtualbox | qemu | hyperv
  desktop = "niri";          # "xfce" / "i3" for VMs without 3D (off by default), "none" for headless
  sharedFolders = false;     # VMware /mnt/hgfs, VirtualBox /media/sf_*
  pentest = { dfir = false; reversing = true; wireless = false; … };
}

The machine
nh os switch -H nixdaemon             # rebuild after an edit: diff, sudo, activate
nix flake update && nh os switch -H nixdaemon   # update everything
sudo nixos-rebuild switch --rollback  # undo the last rebuild (or pick a generation at boot)
nh clean all --keep 5                 # free disk (also runs weekly by itself)
An engagement
htbup                                 # VPN (profiles in ~/.config/htb/vpn/)
htbbox new EscapeTwo 10.10.11.202 win medium sequel.htb dc01.sequel.htb
htbscan full                          # nmap into $BOXDIR/recon, ports into box.json
htbtime                               # fix Kerberos clock skew against the DC
revshell bash                         # payload on stdout, the listener to run on stderr
hcmode kerb                           # which hashcat -m?
htbbox cred sql_svc 'P@ss' mssql      # record as you go
htbbox info                           # the box card: ports, creds, flags, notes
htbcast -n foothold                   # record the terminal for the write-up
pentest-cheat has all of it; pentest-cheat ad, pentest-cheat pivot …
print one section.

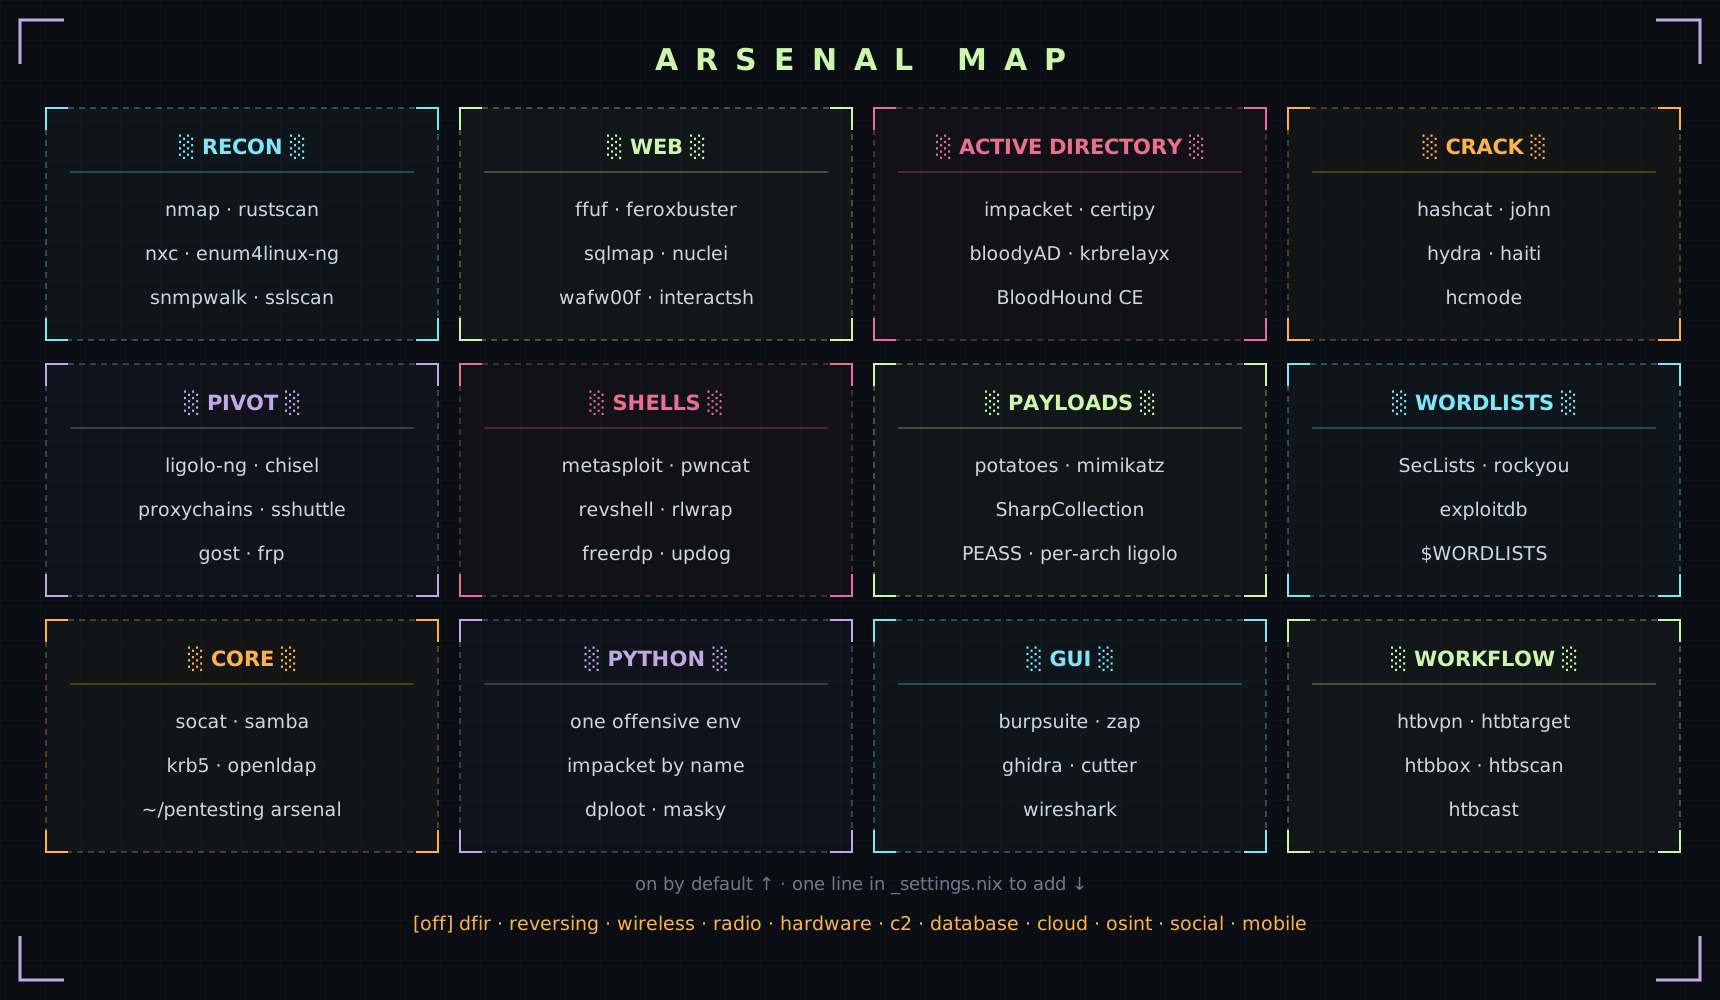
Each category is one file in modules/features/pentest/ and one switch
(daemon.pentest.<name>.enable, set from pentest = { … } in
_settings.nix). Tools go into the system profile, so sudo nmap -sS and
sudo responder just work. nix develop .#pentest-<name> gives you any
category in a throwaway shell without installing it.

Into a toolkit category — add the attribute to the category's packages
list, and its binary name to expectedBins so nix flake check proves it
installed:
# modules/features/pentest/web.nix
packages = pkgs: with pkgs; [
  ffuf gobuster feroxbuster
  wafw00f                     # ← new
];
expectedBins = [ "ffuf" "gobuster" "feroxbuster" "wafw00f" ];
Anything else, just for your machine — add it in
modules/hosts/generic/default.nix under environment.systemPackages.
Finding names: nix search nixpkgs <word>, or https://search.nixos.org.
The attribute and the binary often differ (thc-hydra → hydra, netexec →
nxc, testssl → testssl.sh); expectedBins is where that mismatch gets
caught. Then git add any new file and nh os switch.
A whole new category is one new file calling the category factory
(_sets.nix) plus one line in modules/features/pentest/default.nix; copy
recon.nix as the template.

The flake is dendritic: flake-parts loads every
*.nix under modules/ (via import-tree) as a module, and each file declares
the outputs it owns. Modules refer to each other by name through self, never
by path. Files and directories whose path contains /_ are skipped — that is
where plain data and helper files live.
NixDaemon/
├── flake.nix                     inputs; outputs = import-tree ./modules
├── docs/install.md               installing, every platform
└── modules/
    ├── hosts/
    │   ├── generic/              ← YOUR machine: nixosConfigurations.nixdaemon
    │   │   ├── _settings.nix         the one file you edit
    │   │   ├── _hardware-configuration.nix
    │   │   ├── default.nix           self.lib.mkHost settings → a NixOS system
    │   │   └── home.nix              the shared, self-contained home
    │   └── laptop/               the author's machine (needs his secrets; not for you)
    ├── features/
    │   ├── pentest/              23 categories + the HTB workflow + the arsenal
    │   │   ├── _sets.nix             category factory: package list → module + check + dev shell
    │   │   ├── htb.nix vpn.nix boxes.nix time.nix casts.nix helpers.nix
    │   │   └── payloads.nix paths.nix _pkgs/   the pinned, cross-built arsenal
    │   └── desktop/              niri + noctalia (`nix run .#niri`); xfce.nix, i3.nix, x11.nix for VMs
├── skills/nixdaemon/             the Claude Code skill: system map, traps, diagnosis
    └── home/                     home-manager modules (terminal, prompt, neovim, cheats …)
Two hosts share one toolkit. nixdaemon (generic) is built from
_settings.nix and nothing personal; nixos (the author's laptop) layers his
identity, secrets, dotfiles and hardware fixes on top. The generic host builds
without anyone's keys.

| Symptom | Fix |
|---|---|
| "path does not exist" / missing attribute | git add -A — flakes only see tracked files |
| Black screen after logging in to Niri | no 3D in the VM: desktop = "xfce" or "i3", rebuild from a text console (Ctrl+Alt+F2) |
| Stuck on anything | run claude — the installed nixdaemon skill knows this system's layout and traps |
Failed assertions: _settings.nix: … |
a value is misspelled; the message names it |
| Doesn't boot after install | wrong boot mode or biosDevice; fix from the ISO and re-run nixos-install |
| Build killed / frozen | out of RAM: add --max-jobs 1 --cores 2 |
hash mismatch on a payload |
upstream changed a release file: pentest-update |
| Anything after a rebuild | boot the previous generation; nothing is lost |
More in docs/install.md § 9.
Honest note. NixDaemon is one person's toolkit opened up. The Niri desktop and the toolkit are what get daily use; XFCE, i3, aarch64 and some hypervisor combinations are newer and less tested, so things will not always work flawlessly. Issues and fixes are welcome.

| Where | What |
|---|---|
| docs/install.md | installing on bare metal, every hypervisor, an existing NixOS, or just the tools |
pentest-cheat · cheats/pentest.md |
the toolkit and the HTB workflow, by section |
niri-cheat · cheats/niri.md |
the desktop's keys |
nix-cheat · cheats/nix.md |
rebuilding, updating, rollback, the repo |
| modules/hosts/generic/_settings.nix | every machine setting, commented |
the header comment of each modules/**/*.nix |
why that file is the way it is |

NixDaemon replaces IceBreaker, the earlier NixOS pentest flake (12
categories, XFCE/Hyprland, a setup.sh installer, pipx for the Python
tools). What changed, and what came across:
| IceBreaker | NixDaemon |
|---|---|
setup.sh edits files, then rebuilds |
one _settings.nix, then plain nixos-install / nixos-rebuild |
| pipx installs Python tools at runtime | one pinned Python env; impacket scripts by bare name, collision-guarded |
ligolo-fetch.sh downloads agents |
ligolo-ng, chisel, fscan, pspy cross-built from source per OS/arch |
newbox, flag, cred, ~/targets/ |
htbbox with box.json, writes /etc/hosts, imports nmap XML |
settarget + ~/.target.env |
htbtarget, live in every open terminal at its next prompt |
nmap-init / nmap-allports / nmap-targeted |
htbscan [full|ports|udp], straight into the box |
revshell, hcmode |
carried over: revshell uses the tunnel IP, hcmode searches the installed hashcat |
| presets | pentest = { … } switches in _settings.nix |
| — | nix flake check: every category smoke-tested, VM tests for the HTB helpers |
The section headers, dividers and diagrams on this page are IceBreaker's graphics, redrawn for NixDaemon.
☧ · Rosé Pine all the way down · authorised targets only