overview.md (15933B)
1 --- 2 title: "161/udp, 162/udp, 10161-10162/tcp/udp - Pentesting SNMP" 3 section: "Network Services" 4 sectionSlug: "network-services-pentesting" 5 sourcePath: "src/network-services-pentesting/pentesting-snmp/README.md" 6 sourceUrl: "https://github.com/HackTricks-wiki/hacktricks/blob/188de82beb54e70956b2952367a0af91d26758b8/src/network-services-pentesting/pentesting-snmp/README.md" 7 sha: "188de82beb54e70956b2952367a0af91d26758b8" 8 isIndex: true 9 modified: true 10 license: "CC-BY-NC-4.0" 11 --- 12 13 # 161/udp, 162/udp, 10161-10162/tcp/udp - Pentesting SNMP 14 15 ## Basic Information 16 17 **SNMP (Simple Network Management Protocol)** is used to monitor and, when write access is authorized, configure networked devices such as routers, switches, printers, servers, and IoT systems.<sup>[[4]](#references)</sup> 18 19 ```text 20 PORT STATE SERVICE REASON VERSION 21 161/udp open snmp udp-response ttl 244 ciscoSystems SNMPv3 server (public) 22 ``` 23 24 > [!TIP] 25 > SNMP managers commonly listen on **162/UDP** for asynchronous notifications from agents. A Trap is unacknowledged, while an InformRequest expects a response.<sup>[[4]](#references)</sup> 26 27 ### MIB 28 29 A **Management Information Base (MIB)** is the conceptual collection of managed objects available through SNMP. MIB modules define those objects in a standardized hierarchy using the Structure of Management Information (SMI), an adapted subset of ASN.1. The module definitions describe each object's OID, syntax, access, and semantics; the live values reside in the agent rather than in the definition file.<sup>[[5]](#references)</sup> 30 31 ### OIDs 32 33 **Object Identifiers (OIDs)** play a crucial role. These unique identifiers are designed to manage objects within a **Management Information Base (MIB)**. 34 35 The upper arcs of the OID tree are delegated to standards bodies and other registration authorities. 36 37 Furthermore, vendors are granted the liberty to establish private branches. Within these branches, they have the **autonomy to include managed objects pertinent to their own product lines**. This system ensures that there is a structured and organized method for identifying and managing a wide array of objects across different vendors and standards. 38 39 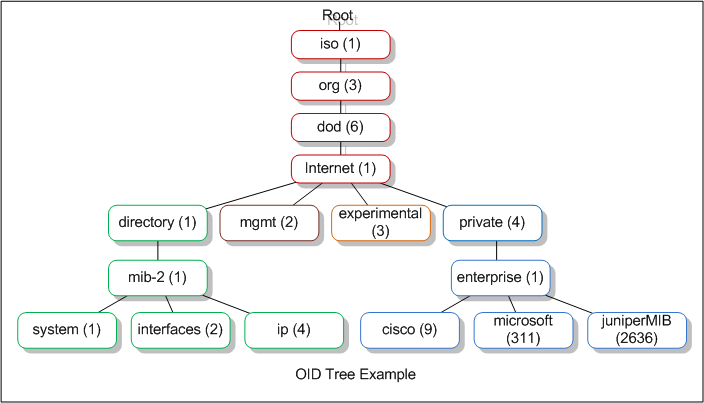 40 41 You can **navigate** through an **OID tree** from the web here: [http://www.oid-info.com/cgi-bin/display?tree=#focus](http://www.oid-info.com/cgi-bin/display?tree=#focus) or **see what a OID means** (like `1.3.6.1.2.1.1`) accessing [http://oid-info.com/get/1.3.6.1.2.1.1](http://oid-info.com/get/1.3.6.1.2.1.1).\ 42 There are some **well-known OIDs** like the ones inside [1.3.6.1.2.1](http://oid-info.com/get/1.3.6.1.2.1) that references MIB-2 defined Simple Network Management Protocol (SNMP) variables. And from the **OIDs pending from this one** you can obtain some interesting host data (system data, network data, processes data...) 43 44 ### **OID Example** 45 46 [**Example from here**](https://www.netadmintools.com/snmp-mib-and-oids/):<sup>[[1]](#references)</sup> 47 48 **`1 . 3 . 6 . 1 . 4 . 1 . 1452 . 1 . 2 . 5 . 1 . 3. 21 . 1 . 4 . 7`** 49 50 Here is a breakdown of this address.<sup>[[1]](#references)</sup> 51 52 - 1 – the `iso` root arc. Not every possible ASN.1 OID starts with 1; the root also defines arcs 0 and 2. 53 - 3 – this is called ORG and it is used to specify the organization that built the device. 54 - 6 – this is the dod or the Department of Defense which is the organization that established the Internet first. 55 - 1 – this is the value of the internet to denote that all communications will happen through the Internet. 56 - 4 – this value determines that this device is made by a private organization and not a government one. 57 - 1 – this value denotes that the device is made by an enterprise or a business entity. 58 59 The prefix `1.3.6.1.4.1` is the widely used `internet.private.enterprises` branch. It is common for vendor-specific objects, but standards-defined objects and other registered branches use different prefixes; the distinction is not simply government versus private devices. 60 61 Moving on to the next set of numbers. 62 63 - 1452 – gives the name of the organization that manufactured this device. 64 - 1 – explains the type of device. In this case, it is an alarm clock. 65 - 2 – determines that this device is a remote terminal unit. 66 67 The rest of the values give specific information about the device. 68 69 - 5 – denotes a discrete alarm point. 70 - 1 – specific point in the device 71 - 3 – port 72 - 21 – address of the port 73 - 1 – display for the port 74 - 4 – point number 75 - 7 – state of the point 76 77 ### SNMP Versions 78 79 The versions most likely to be encountered are: 80 81 - **SNMPv1 and SNMPv2c**: Common community-based models. The community string and management data are not cryptographically protected, so anyone able to observe the traffic can read them. 82 - **SNMPv3**: Separates message processing, security, and access control. Its standard security levels are `noAuthNoPriv`, `authNoPriv`, and `authPriv`; only `authPriv` provides both message authentication and encryption/privacy. Weak authentication secrets may still be susceptible to offline guessing after capturing the required exchange.<sup>[[6]](#references)</sup> 83 84 ### Community Strings 85 86 For community-based SNMPv1/v2c, the requester normally needs an accepted community string; SNMPv3 uses a security name and the credentials required by the configured security level. `public` and `private` are common defaults, not protocol-defined types: 87 88 - **`public`** is conventionally configured read-only. 89 - **`private`** is conventionally configured read-write. 90 91 Note that **the writability of an OID depends on the community string used**, so **even** if you find that "**public**" is being used, you could be able to **write some values.** Also, there **may** exist objects which are **always "Read Only".**\ 92 An unauthorized or invalid SET can return version- and condition-specific errors such as `noAccess`, `notWritable`, `wrongType`, or legacy `noSuchName`/`readOnly` compatibility values.<sup>[[7]](#references)</sup> 93 94 Agents commonly drop SNMPv1/v2c requests with an invalid community string, so a syntactically valid SNMP response is strong evidence that the community was accepted. A timeout alone is inconclusive because filtering, packet loss, rate limiting, and unsupported versions produce the same symptom. 95 96 ## Ports 97 98 [The standard port mappings are]:<sup>[[2]](#references)[[8]](#references)</sup> 99 100 - The SNMP agent receives requests on UDP port **161**. 101 - The manager receives notifications ([Traps](https://en.wikipedia.org/wiki/Simple_Network_Management_Protocol#Trap) and [InformRequests](https://en.wikipedia.org/wiki/Simple_Network_Management_Protocol#InformRequest)) on port **162**. 102 - SNMP over TLS uses TCP **10161/10162**, while SNMP over DTLS uses UDP **10161/10162**; the lower port is for command traffic and the higher port for notifications. 103 104 ## Brute-Force Community String (v1 and v2c) 105 106 To **guess the community string** you could perform a dictionary attack. Check [here different ways to perform a brute-force attack against SNMP](https://github.com/HackTricks-wiki/hacktricks/blob/188de82beb54e70956b2952367a0af91d26758b8/src/generic-hacking/brute-force.md#snmp). A frequently used community string is `public`. 107 108 ## Enumerating SNMP 109 110 Install the relevant MIB definitions to resolve numeric OIDs into names and descriptions: 111 112 ```bash 113 apt-get install snmp-mibs-downloader 114 download-mibs 115 # Finally comment the line saying "mibs :" in /etc/snmp/snmp.conf 116 sudo vi /etc/snmp/snmp.conf 117 ``` 118 119 If you know a valid community string, you can access the data using **SNMPWalk** or **SNMP-Check**: 120 121 ```bash 122 snmpbulkwalk -c [COMM_STRING] -v [VERSION] [IP] . #Don't forget the final dot 123 snmpbulkwalk -c public -v2c 10.10.11.136 . 124 125 snmpwalk -v [VERSION_SNMP] -c [COMM_STRING] [DIR_IP] 126 snmpwalk -v [VERSION_SNMP] -c [COMM_STRING] [DIR_IP] 1.3.6.1.2.1.4.34.1.3 #Get IPv6, needed dec2hex 127 snmpwalk -v [VERSION_SNMP] -c [COMM_STRING] [DIR_IP] NET-SNMP-EXTEND-MIB::nsExtendObjects #get extended 128 snmpwalk -v [VERSION_SNMP] -c [COMM_STRING] [DIR_IP] .1 #Enum all 129 130 snmp-check [DIR_IP] -p [PORT] -c [COMM_STRING] 131 132 nmap --script "snmp* and not snmp-brute" <target> 133 134 braa <community string>@<IP>:.1.3.6.* #Bruteforce specific OID 135 ``` 136 137 If the Net-SNMP `extend` feature is configured and exposed to the tested principal, query its output with: 138 139 ```bash 140 snmpwalk -v X -c public <IP> NET-SNMP-EXTEND-MIB::nsExtendOutputFull 141 ``` 142 143 Depending on the enabled MIB modules and access-control view, SNMP may reveal network interfaces and addresses, usernames, uptime, OS/version information, storage, and running processes. Process command lines or extension output can occasionally expose secrets. 144 145 ### **Dangerous Settings** 146 147 In the realm of network management, certain configurations and parameters are key to ensuring comprehensive monitoring and control. 148 149 ### Access Settings 150 151 Two main settings enable access to the **full OID tree**, which is a crucial component in network management: 152 153 1. **`rwuser USER noauth`** grants the named SNMPv3 security user read-write access at the `noAuthNoPriv` security level. `noauth` means messages need neither authentication nor privacy; it does not remove the required user/security-name mapping. An optional OID or view can restrict the accessible subtree.<sup>[[9]](#references)</sup> 154 2. For more specific control, access can be granted using: 155 - **`rwcommunity`** for **IPv4** addresses, and 156 - **`rwcommunity6`** for **IPv6** addresses. 157 158 These directives require a community string and can optionally restrict the source and accessible OID/view. Without those restrictions, a read-write community can expose every writable object supported by the agent.<sup>[[9]](#references)</sup> 159 160 ### SNMP Parameters for Microsoft Windows 161 162 A series of **Management Information Base (MIB) values** are utilized to monitor various aspects of a Windows system through SNMP: 163 164 - **System Processes**: Accessed via `1.3.6.1.2.1.25.1.6.0`, this parameter allows for the monitoring of active processes within the system. 165 - **Running Programs**: The `1.3.6.1.2.1.25.4.2.1.2` value is designated for tracking currently running programs. 166 - **Processes Path**: To determine where a process is running from, the `1.3.6.1.2.1.25.4.2.1.4` MIB value is used. 167 - **Storage Units**: The monitoring of storage units is facilitated by `1.3.6.1.2.1.25.2.3.1.4`. 168 - **Software Name**: To identify the software installed on a system, `1.3.6.1.2.1.25.6.3.1.2` is employed. 169 - **User Accounts**: The `1.3.6.1.4.1.77.1.2.25` value allows for the tracking of user accounts. 170 - **TCP Local Ports**: Finally, `1.3.6.1.2.1.6.13.1.3` is designated for monitoring TCP local ports, providing insight into active network connections. 171 172 ### Cisco 173 174 For Cisco-specific enumeration, see [Cisco SNMP](/hacktricks/network-services-pentesting/pentesting-snmp/cisco-snmp). 175 176 ## From SNMP to RCE 177 178 If you have a community or SNMPv3 principal that can write sensitive objects, command execution may be possible on agents exposing executable extension MIBs. See [SNMP to RCE](/hacktricks/network-services-pentesting/pentesting-snmp/snmp-rce). 179 180 ## **Massive SNMP** 181 182 [Braa](https://github.com/mteg/braa) is a mass SNMP scanner. Unlike `snmpwalk` from Net-SNMP, it can query many hosts concurrently in one process, which makes it efficient but also easy to run at a disruptive rate. 183 184 Braa implements its own SNMP stack, so it does not require a library such as Net-SNMP. 185 186 **Syntax:** braa \[Community-string]@\[IP of SNMP server]:\[iso id] 187 188 ```bash 189 braa ignite123@192.168.1.125:.1.3.6.* 190 ``` 191 192 This can extract many megabytes of information, so save and filter the output systematically. 193 194 So, lets look for the most interesting information (from [https://blog.rapid7.com/2016/05/05/snmp-data-harvesting-during-penetration-testing/](https://blog.rapid7.com/2016/05/05/snmp-data-harvesting-during-penetration-testing/)):<sup>[[3]](#references)</sup> 195 196 ### **Devices** 197 198 The process begins with the extraction of **sysDesc MIB data** (1.3.6.1.2.1.1.1.0) from each file to identify the devices. This is accomplished through the use of a **grep command**: 199 200 ```bash 201 grep ".1.3.6.1.2.1.1.1.0" *.snmp 202 ``` 203 204 ### **Identify Private String** 205 206 A crucial step involves identifying the **private community string** used by organizations, particularly on Cisco IOS routers. This string enables the extraction of **running configurations** from routers. The identification often relies on analyzing SNMP Trap data for the word "trap" with a **grep command**: 207 208 ```bash 209 grep -i "trap" *.snmp 210 ``` 211 212 ### **Usernames/Passwords** 213 214 Logs stored within MIB tables are examined for **failed logon attempts**, which might accidentally include passwords entered as usernames. Keywords such as _fail_, _failed_, or _login_ are searched to find valuable data: 215 216 ```bash 217 grep -i "login\|fail" *.snmp 218 ``` 219 220 ### **Emails** 221 222 Finally, to extract **email addresses** from the data, a **grep command** with a regular expression is used, focusing on patterns that match email formats: 223 224 ```bash 225 grep -E -o "\b[A-Za-z0-9._%+-]+@[A-Za-z0-9.-]+\.[A-Za-z]{2,6}\b" *.snmp 226 ``` 227 228 ## Modifying SNMP values 229 230 You can use _**NetScanTools**_ to **modify values**. You will need to know the **private string** in order to do so. 231 232 ## Spoofing 233 234 If an ACL authorizes SNMP solely by source IP, a forged UDP source may cause the agent to send a response to that authorized address. The attacker will not receive the response unless they are on-path, control that address, or can otherwise observe/reroute the reply. Stateful filtering and SNMPv3 authentication prevent this from becoming a general read primitive. 235 236 ## Examine SNMP Configuration files 237 238 - snmp.conf 239 - snmpd.conf 240 - snmp-config.xml 241 242 243 ## HackTricks Automatic Commands 244 245 ```text 246 Protocol_Name: SNMP #Protocol Abbreviation if there is one. 247 Port_Number: 161 #Comma separated if there is more than one. 248 Protocol_Description: Simple Network Management Protocol #Protocol Abbreviation Spelled out 249 250 Entry_1: 251 Name: Notes 252 Description: Notes for SNMP 253 Note: | 254 SNMP - Simple Network Management Protocol is a protocol used to monitor different devices in the network (like routers, switches, printers, IoTs...). 255 256 https://book.hacktricks.wiki/en/network-services-pentesting/pentesting-snmp/index.html 257 258 Entry_2: 259 Name: SNMP Check 260 Description: Enumerate SNMP 261 Command: snmp-check {IP} 262 263 Entry_3: 264 Name: OneSixtyOne 265 Description: Crack SNMP passwords 266 Command: onesixtyone -c /usr/share/seclists/Discovery/SNMP/common-snmp-community-strings-onesixtyone.txt {IP} -w 100 267 268 Entry_4: 269 Name: Nmap 270 Description: Nmap snmp (no brute) 271 Command: nmap --script "snmp* and not snmp-brute" {IP} 272 273 Entry_5: 274 Name: Hydra Brute Force 275 Description: Need Nothing 276 Command: hydra -P {Big_Passwordlist} -v {IP} snmp 277 278 279 ``` 280 281 ## References 282 283 - [1] [SNMP MIB and OIDs explained](https://www.netadmintools.com/snmp-mib-and-oids/) 284 - [2] [Simple Network Management Protocol (Wikipedia)](https://en.wikipedia.org/wiki/Simple_Network_Management_Protocol) 285 - [3] [SNMP Data Harvesting During Penetration Testing (Rapid7)](https://blog.rapid7.com/2016/05/05/snmp-data-harvesting-during-penetration-testing/) 286 - [4] [RFC 3413 – SNMP Applications](https://www.rfc-editor.org/rfc/rfc3413) 287 - [5] [RFC 2578 – Structure of Management Information Version 2](https://www.rfc-editor.org/rfc/rfc2578) 288 - [6] [RFC 3411 – Architecture and SNMP security levels](https://www.rfc-editor.org/rfc/rfc3411) 289 - [7] [RFC 3416 – SNMPv2 protocol operations and error statuses](https://www.rfc-editor.org/rfc/rfc3416) 290 - [8] [RFC 6353 – SNMP over TLS and DTLS](https://www.rfc-editor.org/rfc/rfc6353) 291 - [9] [Net-SNMP `snmpd.conf` access-control directives](https://manpages.debian.org/testing/snmpd/snmpd.conf.5.en.html)