ios-testing-environment.md (14617B)
1 --- 2 title: "iOS Testing Environment" 3 section: "Mobile" 4 sectionSlug: "mobile-pentesting" 5 sourcePath: "src/mobile-pentesting/ios-pentesting/ios-testing-environment.md" 6 sourceUrl: "https://github.com/HackTricks-wiki/hacktricks/blob/188de82beb54e70956b2952367a0af91d26758b8/src/mobile-pentesting/ios-pentesting/ios-testing-environment.md" 7 sha: "188de82beb54e70956b2952367a0af91d26758b8" 8 isIndex: false 9 modified: true 10 license: "CC-BY-NC-4.0" 11 --- 12 13 # iOS Testing Environment 14 15 ## Apple Developer Program 16 17 A **provisioning identity** associates signing credentials with an Apple developer account. A paid Apple Developer Program membership currently costs USD 99 per membership year (or a local-currency equivalent), but it is not required for basic personal on-device testing: Xcode can create a free Personal Team profile with an Apple Account. Paid membership is required for distribution and additional capabilities.<sup>[[5]](#references)</sup> 18 19 Xcode can create a **free development provisioning profile** for personal on-device testing. Open **Xcode** → **Settings** (called **Preferences** in older releases) → **Accounts**, add the Apple Account, and use **Manage Certificates** → **+** → **Apple Development** when a development certificate is needed. Select the Personal Team for the target, connect the iPhone, unlock it, and accept the separate **Trust This Computer** pairing prompt before expecting Xcode to deploy the application.<sup>[[5]](#references)</sup><sup>[[8]](#references)</sup> Then allow Xcode to manage signing. On the device, trust the development profile if prompted under **Settings** → **General** → **VPN & Device Management** (called **Profiles & Device Management** on some older iOS releases); trusting the computer and trusting the development profile are distinct steps. 20 21 On **iOS 16+**, **Developer Mode** must also be enabled on the device before locally installed development-signed applications (or apps re-signed with `get-task-allow`) will run. This option only appears **after pairing the device with Xcode** or after installing a development-signed app once. The flow is: **pair the device**, trigger an install from Xcode, then enable **Settings** --> **Privacy & Security** --> **Developer Mode**, reboot, and confirm the prompt after unlock.<sup>[[2]](#references)</sup> 22 23 Apps do not gain shared keychain access merely because they use the same signing certificate. They must be provisioned with a matching keychain access-group entitlement, and a keychain item can be shared only through a group to which each app belongs.<sup>[[6]](#references)</sup> 24 25 The provisioning profiles are stored inside the phone in **`/Library/MobileDevice/ProvisioningProfiles`** 26 27 ### Modern host-side device tooling 28 29 For current iOS testing, the host tooling is increasingly split between: 30 31 - **`xcrun simctl`** for simulator management 32 - **`xcrun xctrace list devices`** to enumerate simulators and physical devices 33 - **`xcrun devicectl`** (Xcode 15+) to interact with paired physical devices from the command line 34 35 Useful examples: 36 37 ```bash 38 # List booted simulators 39 xcrun simctl list | grep Booted 40 41 # List all visible devices/simulators 42 xcrun xctrace list devices 43 44 # List paired physical devices (Xcode 15+) 45 xcrun devicectl list devices 46 ``` 47 48 `devicectl` is especially useful in automation pipelines where you need to install or launch a test build without opening Xcode: 49 50 ```bash 51 xcrun devicectl device install app --device <udid> <path_to_app_or_ipa> 52 xcrun devicectl device launch app --terminate-existing --device <udid> <bundle_id> 53 ``` 54 55 Keep Xcode updated when testing **iOS 17+** devices. Apple moved developer services to the **CoreDevice** stack and also changed how **Developer Disk Images** are handled, so outdated host tooling frequently fails with pairing, image-mounting, or app-launch errors. 56 57 ## **Simulator** 58 59 > [!TIP] 60 > A **simulator is not the same as an emulator**. It runs a platform model intended for development and does not reproduce every hardware-backed security property of a physical device. 61 62 ### **Simulator** 63 64 The first thing you need to know is that **performing a pentest inside a simulator will much more limited than doing it in a jailbroken device**. 65 66 All the tools required to build and support an iOS app are **only officially supported on Mac OS**.\ 67 Apple's de facto tool for creating/debugging/instrumenting iOS applications is **Xcode**. It can be used to download other components such as **simulators** and different **SDK** **versions** required to build and **test** your app.\ 68 It's highly recommended to **download** Xcode from the **official app store**. Other versions may be carrying malware. 69 70 The simulator files can be found in `/Users/<username>/Library/Developer/CoreSimulator/Devices` 71 72 The simulator is still very useful for quickly testing **filesystem artifacts**, **NSUserDefaults**, **plist parsing**, **custom URL schemes**, and **basic runtime instrumentation**. However, keep in mind that it doesn't emulate several physical-device security properties that are often relevant during a pentest, such as the **Secure Enclave**, **baseband**, certain **keychain access-control behaviours**, realistic **biometric flows**, and jailbreak-specific execution conditions. 73 74 To open the simulator, run Xcode, then press in the _Xcode tab_ --> _Open Developer tools_ --> _Simulator_\ 75 \_\_In the following image clicking in "iPod touch \[...]" you can select other device to test in: 76 77 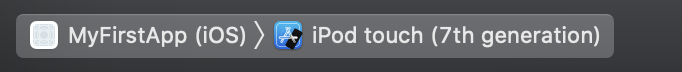 78 79 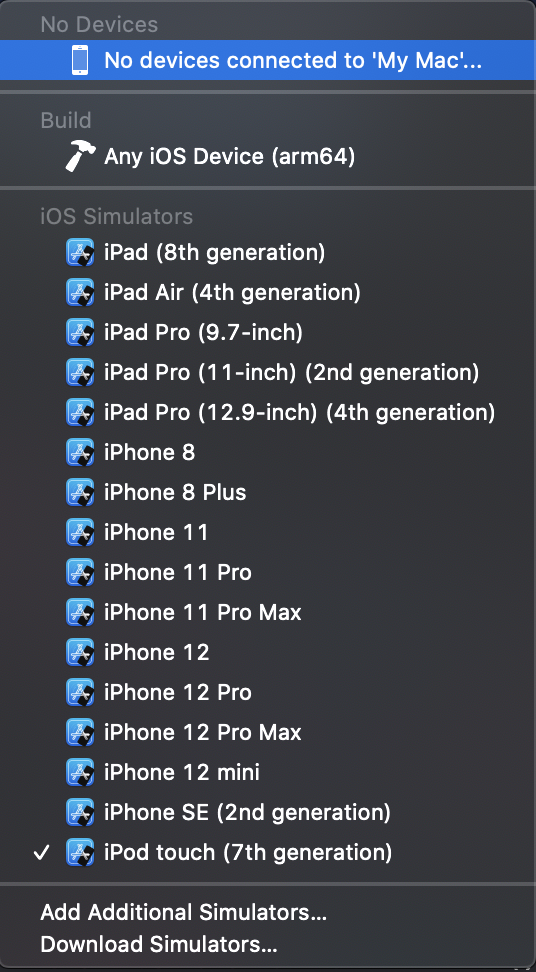 80 81 ### Applications in the Simulator 82 83 Inside `/Users/<username>/Library/Developer/CoreSimulator/Devices` you may find all the **installed simulators**. If you want to access the files of an application created inside one of the emulators it might be difficult to know **in which one the app is installed**. A quick way to **find the correct UID** is to execute the app in the simulator and execute: 84 85 ```bash 86 xcrun simctl list | grep Booted 87 iPhone 8 (BF5DA4F8-6BBE-4EA0-BA16-7E3AFD16C06C) (Booted) 88 ``` 89 90 Once you know the UID the apps installed within it can be found in `/Users/<username>/Library/Developer/CoreSimulator/Devices/{UID}/data/Containers/Data/Application` 91 92 However, surprisingly you won't find the application here. You need to access `/Users/<username>/Library/Developer/Xcode/DerivedData/{Application}/Build/Products/Debug-iphonesimulator/` 93 94 And in this folder you can **find the package of the application.** 95 96 ## Emulator 97 98 Corellium is a commercial virtual iOS environment commonly used for mobile security research. It offers virtual jailbroken and non-jailbroken iOS devices, cloud trials, and multiple product/deployment options.<sup>[[7]](#references)</sup> Older descriptions of it as a per-user SaaS product with no trial are now obsolete, and it should not be described as the only publicly available iOS virtualization option. 99 100 ## No Jailbreak needed 101 102 Check this blog post about how to pentest an iOS application in a **non jailbroken device**: 103 104 105 [Ios Pentesting Without Jailbreak](/hacktricks/mobile-pentesting/ios-pentesting/ios-pentesting-without-jailbreak) 106 107 ## Jailbreaking 108 109 Apple strictly requires that the code running on the iPhone must be **signed by a certificate issued by Apple**. **Jailbreaking** is the process of actively **circumventing such restrictions** and other security controls put in places by the OS. Therefore, once the device is jailbroken, the **integrity check** which is responsible for checking apps being installed is patched so it is **bypassed**. 110 111 > [!TIP] 112 > Unlike Android, **you cannot switch to "Developer Mode"** in iOS to run unsigned/untrusted code on the device. 113 114 ### Android Rooting vs. iOS Jailbreaking 115 116 While often compared, **rooting** on Android and **jailbreaking** on iOS are fundamentally different processes. Rooting Android devices might involve **installing the `su` binary** or **replacing the system with a rooted custom ROM**, which doesn't necessarily require exploits if the bootloader is unlocked. **Flashing custom ROMs** replaces the device's OS after unlocking the bootloader, sometimes requiring an exploit. 117 118 In contrast, iOS devices cannot flash custom ROMs due to the bootloader's restriction to only boot Apple-signed images. **Jailbreaking iOS** aims to bypass Apple's code signing protections to run unsigned code, a process complicated by Apple's continuous security enhancements. 119 120 ### Jailbreaking Challenges 121 122 Jailbreaking iOS is increasingly difficult as Apple patches vulnerabilities quickly. **Downgrading iOS** is only possible for a limited time after a release, making jailbreaking a time-sensitive matter. Devices used for security testing should not be updated unless re-jailbreaking is guaranteed. 123 124 iOS updates are controlled by a **challenge-response mechanism** (SHSH blobs), allowing installation only for Apple-signed responses. This mechanism, known as a "signing window", limits the ability to store and later use OTA firmware packages. The [IPSW Downloads website](https://ipsw.me) is a resource for checking current signing windows. 125 126 ### Jailbreak Varieties 127 128 - **Tethered jailbreaks** require a computer connection for each reboot. 129 - **Semi-tethered jailbreaks** allow booting into non-jailbroken mode without a computer. 130 - **Semi-untethered jailbreaks** require manual re-jailbreaking without needing a computer. 131 - **Untethered jailbreaks** offer a permanent jailbreak solution without the need for re-application. 132 133 ### Jailbreaking Tools and Resources 134 135 Jailbreaking tools vary by iOS version and device. Resources such as [Can I Jailbreak?](https://canijailbreak.com), [The iPhone Wiki](https://www.theiphonewiki.com), and [Reddit Jailbreak](https://www.reddit.com/r/jailbreak/) provide up-to-date information. Examples include: 136 137 - [Checkra1n](https://checkra.in/) for older A7-A11/iOS 12-14 era research devices. 138 - [Palera1n](https://palera.in/) for checkm8-compatible devices (A8-A11) on iOS/iPadOS 15+. 139 - [Dopamine](https://github.com/opa334/Dopamine) for many arm64/arm64e devices on iOS 15/16 using a modern rootless jailbreak. 140 - [Unc0ver](https://unc0ver.dev/) remains relevant mainly for older iOS versions up to 14.8. 141 142 Modifying your device carries risks, and jailbreaking should be approached with caution. 143 144 ### Rootless jailbreaks 145 146 Modern iOS 15+ jailbreaks are commonly **rootless** instead of **rootful**. From a tester perspective, this matters because a lot of older guides still assume that jailbreak files live directly under `/` or `/Library/...`, which is no longer true on many current setups. 147 148 - Rootless jailbreaks avoid modifying the sealed system volume directly. 149 - On palera1n, jailbreak files are typically stored under a randomized path in `/private/preboot/...` and exposed through the stable symlink **`/var/jb`**.<sup>[[3]](#references)</sup> 150 - Tweaks, launch daemons, and helper binaries might therefore exist under **`/var/jb`** instead of the legacy rootful locations. 151 152 This has a direct impact on **environment validation**, **Frida setup**, and **jailbreak detection bypass**: 153 154 - When checking whether your tooling installed correctly, inspect both legacy paths and **`/var/jb`**. 155 - When reviewing jailbreak detection logic in an app, remember that modern checks often look for **rootless** artifacts and symlinks in addition to classic indicators like `Cydia.app`. 156 - If a third-party script or tweak assumes a rootful filesystem layout, it may fail silently on a rootless device. 157 158 ### Jailbreaking Benefits and Risks 159 160 Jailbreaking expands the tester's access and permits unsigned tooling or tweaks, but it does not automatically remove the sandbox from every ordinary app. Filesystem access depends on the jailbreak environment, the process's entitlements, and any injected tooling. Jailbreaking also introduces security and stability risks. 161 162 ### **After Jailbreaking** 163 164 165 [Basic Ios Testing Operations](/hacktricks/mobile-pentesting/ios-pentesting/basic-ios-testing-operations) 166 167 ### **Jailbreak Detection** 168 169 **Several applications will try to detect if the mobile is jailbroken and in that case the application won't run**<sup>[[1]](#references)</sup> 170 171 - After jailbreaking an iOS **files and folders are usually installed**, these can be searched to determine if the device is jailbroken. 172 - In modern **rootless** jailbreaks, those files may appear under **`/var/jb`** or resolve through symlinks into `/private/preboot/...` instead of only in classic rootful locations. 173 - In a jailbroken device applications get **read/write access to new files** outside the sandbox 174 - Some **API** **calls** will **behave differently** 175 - The presence of the **OpenSSH** service 176 - Calling `/bin/sh` will **return 1** instead of 0 177 178 **More information about how to detect jailbreaking** [**here**](https://www.trustwave.com/en-us/resources/blogs/spiderlabs-blog/jailbreak-detection-methods/)**.**<sup>[[4]](#references)</sup> 179 180 ## **Jailbreak Detection Bypass** 181 182 - You can try to bypass these detections using **Objection's** `ios jailbreak disable` command. 183 - You could also install the tool **Liberty Lite** (https://ryleyangus.com/repo/). Once the repo is added, the app should appear in the ‘Search’ tab 184 185 ## References 186 187 - [1] [iOS Security Testing - OWASP MASTG](https://mas.owasp.org/MASTG/0x06b-iOS-Security-Testing/) 188 - [2] [Enabling Developer Mode on a Device - Apple Developer Documentation](https://developer.apple.com/documentation/xcode/enabling-developer-mode-on-a-device) 189 - [3] [palera1n v2.0.1 release notes – rootless preboot and `/var/jb`](https://github.com/palera1n/palera1n/releases/tag/v2.0.1) 190 - [4] [Jailbreak Detection Methods](https://www.trustwave.com/en-us/resources/blogs/spiderlabs-blog/jailbreak-detection-methods/) 191 - [5] [Apple Developer – Choosing a Membership](https://developer.apple.com/support/compare-memberships/) 192 - [6] [Apple Developer – Configuring keychain sharing](https://developer.apple.com/documentation/xcode/configuring-keychain-sharing) 193 - [7] [Corellium Support – General FAQs](https://support.corellium.com/troubleshooting-faqs/general-faqs) 194 - [8] [Apple Support – About the “Trust This Computer” alert](https://support.apple.com/en-us/109054)