objection-tutorial.md (14242B)
1 --- 2 title: "Objection Tutorial" 3 section: "Mobile" 4 sectionSlug: "mobile-pentesting" 5 sourcePath: "src/mobile-pentesting/android-app-pentesting/frida-tutorial/objection-tutorial.md" 6 sourceUrl: "https://github.com/HackTricks-wiki/hacktricks/blob/188de82beb54e70956b2952367a0af91d26758b8/src/mobile-pentesting/android-app-pentesting/frida-tutorial/objection-tutorial.md" 7 sha: "188de82beb54e70956b2952367a0af91d26758b8" 8 isIndex: false 9 modified: true 10 license: "CC-BY-NC-4.0" 11 --- 12 13 # Objection Tutorial 14 15 ## **Introduction** 16 17 **objection - Runtime Mobile Exploration** 18 19 [**Objection**](https://github.com/sensepost/objection) is a runtime mobile exploration toolkit, powered by [Frida](https://www.frida.re). It was built with the aim of helping assess mobile applications and their security posture without the need for a jailbroken or rooted mobile device.<sup>[[1]](#references)</sup> 20 21 **Note:** This is not some form of jailbreak / root bypass. By using `objection`, you are still limited by all of the restrictions imposed by the applicable sandbox you are facing. 22 23 ### Summary 24 25 The goal of **objection** is to expose common Frida-powered mobile-testing actions through a reusable command-line interface, reducing the need to write a separate script for every application. 26 27 ## Tutorial 28 29 For this tutorial I am going to use the APK that you can download here: 30 31 [App Release.Zip](https://raw.githubusercontent.com/HackTricks-wiki/hacktricks/188de82beb54e70956b2952367a0af91d26758b8/src/mobile-pentesting/android-app-pentesting/frida-tutorial/app-release.zip) 32 33 Or from its [original repository](https://github.com/asvid/FridaApp) (download app-release.apk) 34 35 ### Installation 36 37 ```bash 38 pip3 install objection 39 ``` 40 41 ### Connection 42 43 Establish a regular **ADB connection**, start **Frida Server** on the device, and verify that the client and server can communicate. 44 45 If you are using a **rooted device** and `frida-server`, enumerate packages and then start the current `objection` REPL (`start` is the modern syntax; older writeups may still show `explore` or `--gadget`): 46 47 ```bash 48 frida-ps -Uai 49 objection -n asvid.github.io.fridaapp start 50 ``` 51 52 If you are using a **non-rooted device**, a common workflow is to patch the APK to embed **Frida Gadget**, reinstall it, and then connect to `Gadget`:<sup>[[3]](#references)</sup> 53 54 ```bash 55 objection patchapk -s app-release.apk --network-security-config --enable-debug --use-aapt2 56 adb install -r app-release.objection.apk 57 objection -n Gadget start 58 ``` 59 60 For a complete Gadget embedding workflow (including `--gadget-config` and `-l`/script-mode patching), check: 61 62 [Readme](/hacktricks/mobile-pentesting/android-app-pentesting/frida-tutorial/overview) 63 64 If the application still crashes or exits as soon as Objection/Frida attaches, continue with [this anti-instrumentation workflow](/hacktricks/mobile-pentesting/android-app-pentesting/android-anti-instrumentation-and-ssl-pinning-bypass). 65 66 ### Basic Actions 67 68 This tutorial lists a practical subset of Objection commands. 69 70 #### Environment 71 72 The environment may reveal interesting information such as paths or accidentally exposed secrets. 73 74 ```bash 75 env 76 ``` 77 78  79 80 #### Frida Information 81 82 ```bash 83 frida 84 ``` 85 86  87 88 #### Upload/Download 89 90 ```bash 91 file download <remote path> [<local path>] 92 file upload <local path> [<remote path>] 93 ``` 94 95 #### Import frida script 96 97 ```bash 98 import <local path frida-script> 99 ``` 100 101 #### Jobs 102 103 Imported scripts and many hooks run as **jobs** in the background, so you can keep using the REPL while the hook stays loaded: 104 105 ```bash 106 import ssl-bypass.js "ssl-bypass" 107 jobs list 108 jobs kill <job_id> 109 ``` 110 111 This is especially useful after `android hooking watch ...` or when importing a long-running Frida helper. 112 113 #### Early instrumentation 114 115 If the app runs root checks, SSL pinning or anti-tampering **during startup**, run the hook before the REPL finishes collecting environment data:<sup>[[2]](#references)</sup> 116 117 ```bash 118 objection -n asvid.github.io.fridaapp start --startup-command "android sslpinning disable" 119 objection -n asvid.github.io.fridaapp start --startup-script ssl-bypass.js 120 ``` 121 122 This is much more reliable when the interesting code runs inside `Application.onCreate()` or in the first launched Activity. 123 124 #### SSLPinning 125 126 ```bash 127 android sslpinning disable #Attempts to disable SSL Pinning on Android devices. 128 ``` 129 130 #### Root detection 131 132 ```bash 133 android root disable #Attempts to disable root detection on Android devices. 134 android root simulate #Attempts to simulate a rooted Android environment. 135 ``` 136 137 #### Exec Command 138 139 ```bash 140 android shell_exec whoami 141 ``` 142 143 #### Screenshots 144 145 ```bash 146 android ui screenshot /tmp/screenshot 147 android ui FLAG_SECURE false #This may enable you to take screenshots using the hardware keys 148 ``` 149 150 #### Useful Android helpers 151 152 ```bash 153 android deoptimize # Force ART to go through the interpreter and make hooks more reliable 154 android proxy set 192.168.1.10 8080 # Set a proxy only for the hooked app 155 android intent implicit_intents --dump-backtrace 156 ``` 157 158 `android deoptimize` is especially useful when ART optimization makes a hook appear correct but the implementation is never reached. 159 160 ### Static analysis made Dynamic 161 162 In a real application we should know all of the information discovered in this part before using objection thanks to **static analysis**. Anyway, this way maybe you can see **something new** as here you will only have a complete list of classes, methods and exported objects. 163 164 This is also useful when you cannot obtain readable source code for the app. 165 166 #### List activities, receivers and services 167 168 ```bash 169 android hooking list activities 170 ``` 171 172  173 174 ```bash 175 android hooking list services 176 android hooking list receivers 177 ``` 178 179 Frida will report an error if none is found. 180 181 #### Getting current activity 182 183 ```bash 184 android hooking get current_activity 185 ``` 186 187  188 189 #### Search Classes 190 191 Start by looking for classes inside the application: 192 193 ```bash 194 android hooking search classes asvid.github.io.fridaapp 195 ``` 196 197  198 199 #### Search Methods of a class 200 201 Now extract the methods inside the `MainActivity` class: 202 203 ```bash 204 android hooking search methods asvid.github.io.fridaapp MainActivity 205 ``` 206 207  208 209 #### List declared Methods of a class with their parameters 210 211 List the declared methods and their parameter types: 212 213 ```bash 214 android hooking list class_methods asvid.github.io.fridaapp.MainActivity 215 ``` 216 217  218 219 #### List classes 220 221 You can also list every class loaded in the current application: 222 223 ```bash 224 android hooking list classes # More classes appear as the application loads additional code. 225 android hooking list class_loaders 226 ``` 227 228 This is useful when you know a class name but not its owning module; locate the class first, then hook its method. 229 230 `android hooking list class_loaders` is especially useful in packed apps, plugins, and apps that decrypt or load additional DEX files at runtime, because interesting classes may appear only in a secondary class loader. 231 232 ### Hooking being easy 233 234 #### Hooking (watching) a method 235 236 The application's [source code](https://github.com/asvid/FridaApp/blob/master/app/src/main/java/asvid/github/io/fridaapp/MainActivity.kt) shows that `MainActivity.sum()` runs every second. Dump its arguments, return value, and backtrace each time it is called: 237 238 ```bash 239 android hooking watch class_method asvid.github.io.fridaapp.MainActivity.sum --dump-args --dump-backtrace --dump-return 240 ``` 241 242  243 244 #### Hooking (watching) an entire class 245 246 To observe the whole `MainActivity` class, hook every method. This can crash the application. 247 248 ```bash 249 android hooking watch class asvid.github.io.fridaapp.MainActivity --dump-args --dump-return 250 ``` 251 252 If you play with the application while the class is hooked you will see when **each function is being called**, its **arguments** and the **return** value. 253 254  255 256 #### Changing boolean return value of a function 257 258 The source shows that `checkPin` accepts a `String` and returns a Boolean. Make the function **always return true**: 259 260  261 262 After the hook is active, any value entered in the PIN field is accepted: 263 264  265 266 ### Class instances 267 268 Search for and print **live instances of a specific Java class**, specified by a fully qualified class name. The returned **hashcode** can then be reused to inspect the object and even execute instance methods on it. 269 270 ```bash 271 android heap search instances <class> 272 android heap print fields <hashcode> 273 android heap print methods <hashcode> --without-arguments 274 android heap execute <hashcode> <method> --return-string 275 android heap evaluate <hashcode> 276 ``` 277 278 This is very useful when static analysis shows an interesting singleton or manager object already in memory and you want to inspect its state or call a helper method without writing a custom Frida script. 279 280  281 282 ### Keystore/Intents 283 284 You can play with the keystore and intents using: 285 286 ```bash 287 android keystore list 288 android intent launch_activity 289 android intent launch_service 290 ``` 291 292 ### Memory 293 294 #### Dump 295 296 ```bash 297 memory dump all <local destination> #Dump all memory 298 memory dump from_base <base_address> <size_to_dump> <local_destination> #Dump a part 299 ``` 300 301 #### List 302 303 ```bash 304 memory list modules 305 ``` 306 307 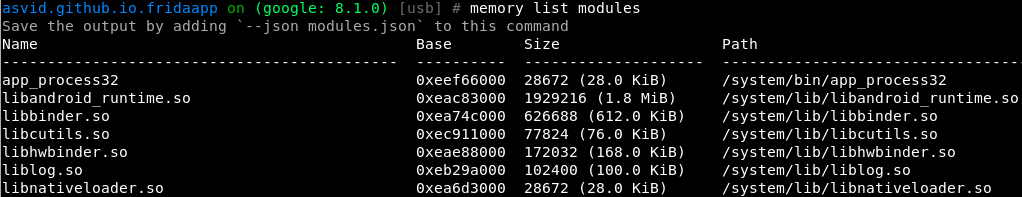 308 309 At the bottom of the list, you can see Frida: 310 311  312 313 List the exports from a selected module: 314 315 ```bash 316 memory list exports libfoo.so 317 memory list exports libfoo.so --json exports.json 318 ``` 319 320 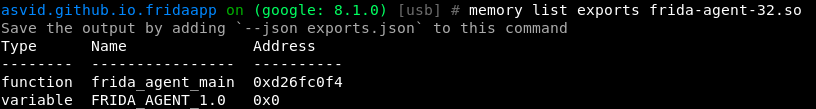 321 322 #### Search/Write 323 324 You can also search and write process memory with Objection: 325 326 ```bash 327 memory search "<pattern eg: 41 41 41 ?? 41>" (--string) (--offsets-only) 328 memory write "<address>" "<pattern eg: 41 41 41 41>" (--string) 329 ``` 330 331 ### SQLite 332 333 Use the `sqlite` command to interact with SQLite databases. 334 335 ```bash 336 sqlite connect /data/data/<package>/databases/app.db 337 sqlite connect /data/data/<package>/databases/app.db --sync 338 ``` 339 340 Using `--sync` will upload the modified temporary copy back to the application path when you exit the SQLite prompt. 341 342 ### Exit 343 344 ```bash 345 exit 346 ``` 347 348 ## What I miss in Objection 349 350 - The hooking methods sometimes crashes the application (this is also because of Frida or anti-instrumentation checks in the target app). 351 - Modern versions can inspect heap instances and execute methods on existing handles, but creating fresh Java objects or orchestrating complex overloaded method calls is usually still easier with a custom Frida script. 352 - There is no shortcut comparable to `sslpinning` for hooking every common cryptographic API and displaying ciphertext, plaintext, keys, IVs, and algorithms. 353 354 ## References 355 356 - [1] [Objection (SensePost)](https://github.com/sensepost/objection) 357 - [2] [Objection wiki: Early Instrumentation](https://github.com/sensepost/objection/wiki/Early-Instrumentation) 358 - [3] [Objection wiki: Patching Android Applications](https://github.com/sensepost/objection/wiki/Patching-Android-Applications)